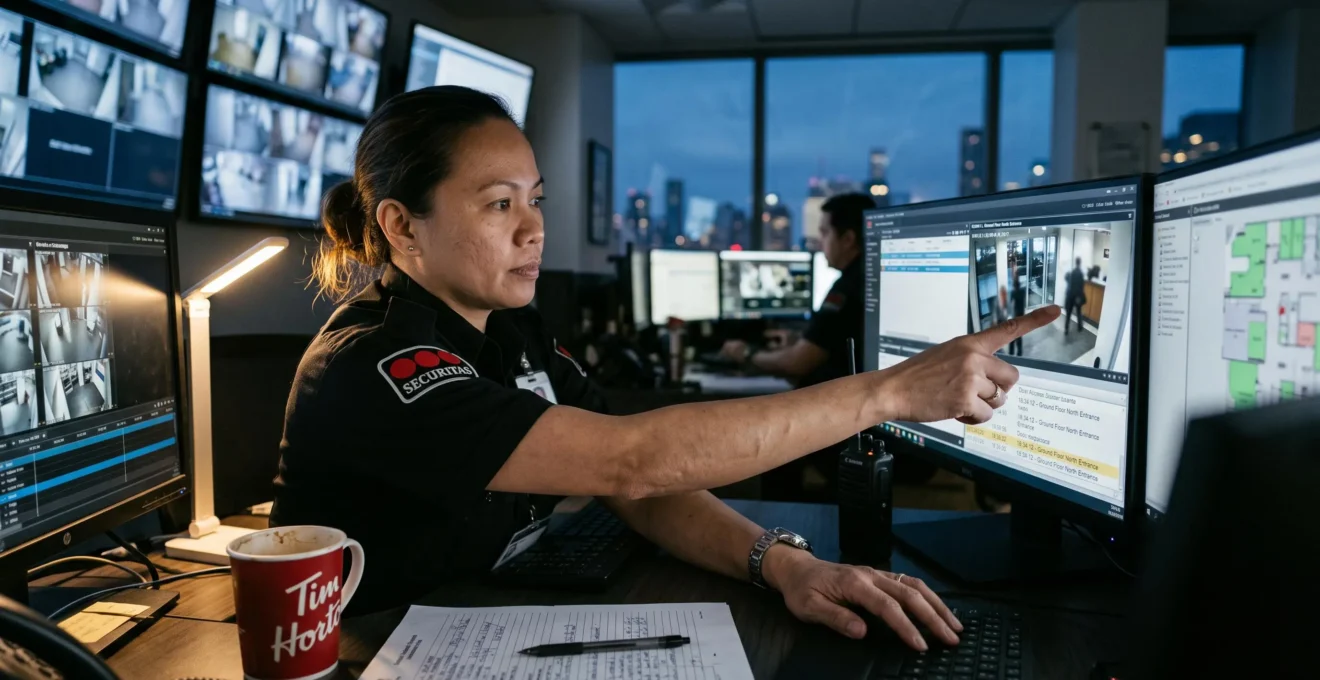
An unauthorized entry is reported at a Canadian office building. Security personnel review camera footage, question employees and inspect door access records. Yet the investigation stalls because the relevant controller stopped reporting events overnight. Without reliable timestamps, credential identifiers and system status information, investigators cannot confidently reconstruct the sequence of activity.
Detailed building access audit trails help facility managers establish what an access control system recorded, when events occurred and which credentials or doors were involved. When correlated with surveillance footage, alarm records and documented response actions, those trails support incident reconstruction, internal accountability and evidence preservation.
However, a badge transaction does not independently establish who physically crossed a doorway. Credentials can be shared, stolen or misused, and some systems cannot confirm that a successful unlock resulted in actual entry. Investigations therefore require multiple corroborating records.
For Canadian organizations operating one building or several locations, the objective is to maintain an accessible, accurate and appropriately protected record of security activity without retaining identifiable movement information indefinitely.
Building Access Audit Trails: Key Points
- Capture successful and denied access attempts, equipment failures and relevant operator actions before an incident occurs.
- Synchronize system clocks and correlate access records with video, alarms and response histories to reconstruct events reliably.
- Centralize investigations while controlling credential permissions, evidence exports and personal information retention.
- Why Missing Entry Records Complicate Workplace Security Investigations
- How to Consolidate Door Access Logs Across Several Office Locations
- Real-Time Access Alerts or Historical Logs for Sensitive Facilities?
- Why Incorrect Clock Synchronization Can Undermine Access Log Evidence
- When Should Canadian Businesses Delete Historical Building Access Logs?
- How Centralized Credential Management Reduces Multi-Site Access Errors
- The Export Mistakes That Can Compromise Security Video Evidence
- How a Centralized Security Management Interface Improves Multi-Site Operations
Why Missing Entry Records Complicate Workplace Security Investigations
Missing entry records weaken workplace security investigations because they prevent investigators from establishing a dependable chronology of credential activity. Without a complete event history, security teams must rely more heavily on witness accounts, video footage and indirect evidence. This can delay findings, leave important questions unresolved and reduce confidence in decisions based on the investigation.
A reliable access trail connects an event timestamp to a particular access point, credential and system result. Investigators can then compare that transaction with video footage, alarm events, employee schedules and visitor registration information.
When a record disappears, the investigative consequences depend on what is missing. An absent timestamp obscures sequence. A missing credential identifier prevents attribution to an issued badge. Unrecorded denied attempts conceal potentially significant activity before a successful entry.
The Canadian Centre for Cyber Security physical and environmental protection guidance addresses physical access audit logging, monitoring, suspicious access activity and coordination with incident-response functions. Its security controls provide a useful reference for building-security programs, although they are not universally binding rules for every Canadian private-sector workplace.
Different investigations require different evidentiary assessments. An internal HR inquiry may use access records to assess whether an employee’s credential was active near an incident. An insurer, lawyer or police investigator may need additional information about the system’s reliability, the preservation of records and how access data was obtained.
Neither a missing badge event nor a damaged audit trail automatically makes a Canadian police report unusable. It instead creates an evidentiary limitation that must be disclosed and evaluated alongside other information.
Hypothetical Case: An Unresolved After-Hours Theft
A facilities manager in an Ontario office building discovers missing equipment on Monday morning. Camera footage shows someone approaching a restricted storage door late Friday, but the person’s face is not visible. The door controller was offline during part of the evening, and locally stored badge transactions were overwritten before the investigation began.
The investigation cannot establish whether an authorized credential unlocked the door. A complete controller history, communication-failure events, credential assignments, door-position records and synchronized footage could have narrowed the uncertainty. Even together, they would not necessarily prove the identity of the person who entered.
To assess exposure before a real incident, facility managers should determine whether they can retrieve the complete history of a selected doorway and date promptly, confirm that denied attempts are recorded, and identify whether outages create detectable gaps.
They should also verify that records remain available after local storage reaches capacity and that investigations can distinguish a genuine absence of activity from missing data.
Once record completeness is established, the next challenge is making those records comparable across buildings and systems.
How to Consolidate Door Access Logs Across Several Office Locations
Consolidating access logs across several office locations requires a common event structure, consistent timestamps and a reliable method for linking credentials to individual identity records. Simply copying logs into one database is insufficient. Investigators must be able to search across sites, distinguish duplicate events and recognize periods when records are incomplete or awaiting synchronization.
Consider an organization with offices in Toronto, Calgary and Vancouver. Each location may use different controllers, reader configurations and local time settings. A cross-site investigation becomes difficult when event exports contain inconsistent identifiers and timestamps without timezone information.
The first step is to normalize records without discarding their original values. Store a standardized timestamp, preferably in UTC, together with the source timestamp, original timezone or offset and the originating device identifier. This preserves information needed to explain discrepancies.
The second step is identity reconciliation. One employee may hold separate credentials issued by different locations. A central directory can associate those identifiers with one person record while retaining the original credential references and assignment history.
An investigable event record should contain enough information to answer who or what was involved, where the activity occurred, when it was recorded and how the system responded.
| Field | Investigative purpose | Validation requirement |
|---|---|---|
| Event timestamp | Places activity on a timeline | Known timezone and verified clock status |
| Site, controller and door | Identifies the access point | Stable asset identifiers |
| Credential or user reference | Supports credential tracing | Historical assignment information |
| Event type and decision | Distinguishes granted, denied and fault events | Consistent event classifications |
| Entry method | Distinguishes badge, PIN or other supported methods | Actual device capability recorded |
| Source event identifier | Supports duplicate detection | Preserved original record |
| Ingestion and synchronization status | Reveals delayed or missing records | Monitored communication health |
This is a recommended operational schema, not a mandatory Canadian legal specification. Its precise implementation depends on the access system and the events that its hardware can capture.
Log consolidation must also handle redundant readers and intermittent connections. Identical-looking events may represent either duplicate transmissions or separate badge presentations. Deduplication rules should use original event identifiers and device context rather than timestamps alone.
Organizations should evaluate aggregation architectures according to their actual operating constraints.
| Architecture | Potential advantages | Issues to validate |
|---|---|---|
| On-premises | Direct control of local infrastructure and storage | Multi-site connectivity, backups, maintenance and export access |
| Cloud-based | Centralized access and potentially simpler cross-site searching | Provider safeguards, data location, outages, permissions and contractual export rights |
| Hybrid | Local event collection with centralized analysis | Synchronization delays, duplicate records and consistency between repositories |
The appropriate design depends on system compatibility, connectivity, organizational policies and applicable privacy requirements. A centralized repository also broadens the consequences of unauthorized data access because it can contain movement information from multiple workplaces.
The NIST Guide to Computer Security Log Management provides foundational technical guidance for enterprise log collection and management. Its principles can inform access-log consolidation, but physical access implementations still require system-specific validation.
With the historical record unified, security teams can decide which events also require immediate operational intervention.
Real-Time Access Alerts or Historical Logs for Sensitive Facilities?
Real-time access alerts and historical logs serve different security purposes. Alerts support rapid intervention when a suspicious event occurs, while historical records support subsequent reconstruction and accountability. Sensitive facilities generally benefit from both, but the level of alerting should reflect the potential consequences of an incident, staffing arrangements and the organization’s ability to respond.
An access-denied event at a routinely used office entrance does not necessarily require an immediate response. The same event at an unoccupied laboratory, followed by a forced-door alarm, may require escalation.
Real-time alerts should therefore prioritize events with meaningful operational consequences. Historical logging should remain comprehensive enough to establish surrounding circumstances, including events that did not individually meet an alert threshold.
| Access point | Real-time alert priority | Historical evidence priority |
|---|---|---|
| Public reception entrance | Exception-based alerts for unusual activity | Entry events, faults and relevant visitor records |
| Server room | High for forced entry or unauthorized access attempts | Detailed credential and door-event history |
| Laboratory or restricted storage | High for defined security exceptions | Correlated entry, alarm and operational records |
| After-hours office floor | Conditional on schedule and occupancy | Entries, denials and schedule-related context |
| Cash-handling area | High for selected access violations | Detailed access history and supporting surveillance references |
Alert fatigue develops when monitoring systems produce more notifications than operators can meaningfully assess. Security teams should classify events by severity, suppress verified technical duplicates and periodically review thresholds against actual incident patterns.
Alert delivery is not equivalent to incident response. A notification reaching an unattended mailbox at 2 a.m. provides little immediate protection unless an on-call procedure directs someone to acknowledge, assess and escalate it.
Every critical alert should have an assigned response owner, an escalation route and a documented acknowledgement process. The organization should also define what happens when communications fail or the primary responder is unavailable.
During an investigation, the historical access record establishes the sequence of system events. Alert history adds another dimension: whether a warning was generated, where it was sent, whether someone acknowledged it and what action followed.
These records may assist internal reviews and discussions with legal counsel or insurers. They do not independently establish that a particular response met every applicable legal, contractual or professional obligation.
Both alert histories and access transactions depend on another basic requirement: trustworthy event timestamps.
Why Incorrect Clock Synchronization Can Undermine Access Log Evidence
Incorrect clock synchronization can undermine access evidence because different security systems may place related events in the wrong sequence. If a door controller, camera recorder and alarm panel disagree about the time, an investigator may incorrectly associate a credential event with unrelated footage or misinterpret the order of an intrusion, alarm and security response.
For example, a controller could record a granted access event at 21:14 while the corresponding camera system displays 21:19. Without documented clock information, investigators cannot immediately establish whether those events occurred together.
Discrepancies become more consequential when several Canadian sites operate across timezones or when daylight saving time changes are handled inconsistently.
The operational objective is to establish a traceable time reference across controllers, video systems, alarm panels and central monitoring infrastructure.
A practical configuration uses an authoritative time source and supported synchronization mechanisms such as Network Time Protocol (NTP). Systems should also record timezone settings, synchronize reliably after connectivity interruptions and retain information about any known clock deviation.
Facility teams should check time accuracy during regular maintenance and after changes likely to affect device configuration, including relevant firmware updates, controller replacement and power-related faults.
Documented clock drift is different from unexplained clock drift. A stable offset may be accounted for when reconstructing events, provided there is reliable evidence of its value during the relevant period. An unknown offset that changes unpredictably creates much greater uncertainty.
For this reason, maintenance records should include the device identifier, reference time, measured deviation, person performing the check and any corrective action.
Five Actions to Verify Access-Control Timestamp Reliability
- Inventory time-dependent systems. Produce a device register identifying every relevant controller, recorder and alarm panel.
- Document synchronization settings. Record the configured time source, timezone and synchronization method for each device.
- Compare related events. Retrieve one access transaction and its corresponding video interval, then produce a timestamp comparison record.
- Investigate discrepancies. Record unexplained offsets and corrective actions in a maintenance findings log.
- Verify corrections. Repeat the event comparison after remediation and retain dated evidence of the result.
The acceptance threshold for clock deviation should be defined according to investigative needs and system capabilities rather than relying on an unsupported universal tolerance.
Once event chronology can be trusted, the organization must determine how long the information should remain available.
When Should Canadian Businesses Delete Historical Building Access Logs?
Canadian businesses should delete identifiable building access logs when they are no longer needed for legitimate documented purposes, subject to applicable legal obligations and preservation requirements. There is no single universal retention period covering every private-sector access system. The appropriate schedule depends on the information collected, incident-discovery needs, employment context, relevant privacy legislation and foreseeable disputes.
Access-control events can contain personal information because they may associate an identifiable person with a location and time. Maintaining these records indefinitely creates privacy and security risks that must be balanced against genuine investigation requirements.
The Office of the Privacy Commissioner of Canada‘s PIPEDA retention guidance explains the importance of retaining personal information only as long as necessary, documenting retention and destruction procedures, and securely disposing of information no longer required.
However, PIPEDA does not govern every Canadian private-sector employment-data activity. Quebec, Alberta and British Columbia have relevant provincial private-sector privacy legislation, and other jurisdictional or sector-specific rules may apply. Organizations should establish which legal regime governs their particular records before finalizing a schedule.
A defensible policy distinguishes categories of information rather than assigning an arbitrary identical period to every record.
| Record category | Retention considerations | Disposal approach |
|---|---|---|
| Routine granted entries | Operational verification, incident-discovery window and applicable requirements | Scheduled secure deletion after the justified period |
| Denied access attempts | Security investigation needs and patterns of attempted misuse | Defined security-event retention rules |
| Forced-door and critical alarm events | Incident severity, investigation status and potential claims | Extended preservation only where justified |
| Employee movement history | Identifiability, workplace privacy and stated collection purposes | Purpose-limited retention and appropriate de-identification where feasible |
| Records associated with an active dispute | Applicable preservation duties and anticipated proceedings | Controlled preservation pending authorized release |
This framework deliberately does not prescribe fixed durations. Each organization must determine defensible periods through documented legal, privacy and operational assessment.
Retention policy must also address the mechanics of deletion. A central platform may remove a record while a local controller, backup or exported incident folder still contains a copy. Disposal procedures should therefore identify all relevant repositories and the technical limitations of deletion from backups.
Legal preservation requirements take precedence over routine deletion schedules when applicable. Records relevant to an existing or reasonably anticipated dispute may require preservation while the matter is assessed. The organization should obtain appropriate legal guidance rather than automatically purging potentially relevant evidence.
An effective written policy specifies record categories, purposes, authorized retention periods, responsible approvers, access controls, disposal methods, exception handling and deletion verification. Employees should also receive appropriate information about workplace data collection and use.
Anonymized or aggregated data may support longer-term operational analysis when re-identification risks are sufficiently addressed. Such data cannot always replace original event histories in a specific security investigation.
Retention decisions become easier to enforce when credential identities and permissions are governed consistently across the organization.
How Centralized Credential Management Reduces Multi-Site Access Errors
Centralized credential management reduces multi-site access errors by maintaining a consistent identity and authorization process across buildings. Instead of allowing each location to independently create and revoke permissions, a shared directory connects credentials to current employment or contractor status. This reduces conflicting access assignments, forgotten badges and unexplained entries associated with outdated permissions.
Imagine an employee moving from a Calgary office to a new role in Toronto. Under separate local administration, the Toronto team may issue a new badge while the old Calgary permissions remain active. Months later, an unexplained Calgary access event could involve a credential that should already have been disabled.
Similar risks arise when contractor engagements end, temporary permissions expire or employees take extended leave without a coordinated access review.
A centralized identity model uses one authoritative person record linked to all relevant credentials. Role-based access profiles can then define which buildings and restricted areas the individual may access.
When HR or contractor management records change, a documented workflow should evaluate and update the corresponding physical access permissions. The workflow should cover new hires, role transfers, suspensions, departures and time-limited assignments.
Deprovisioning speed is an important control. Leaving a former employee’s credentials active for several days unnecessarily extends the period during which those credentials could be misused. The appropriate deadline should be defined according to organizational risk and operating requirements, with urgent revocations handled accordingly.
Audit indicators can expose failures that ordinary provisioning reports overlook.
- Active credentials compared with current authorized personnel at each site.
- Credentials with permissions at buildings their holders no longer need to access.
- Elapsed time between an HR status change and corresponding access revocation.
- Dormant badges that remain enabled despite extended inactivity.
- Temporary credentials that remain active beyond their approved purpose.
These indicators require contextual review. An employee legitimately assigned to emergency response may need access to a rarely visited location, while an unused badge could represent either an authorized backup or an administrative oversight.
Central identity management also improves investigations by preserving historical relationships between a credential, its assigned holder and applicable permissions at the time of an event. Current assignments should not overwrite the historical context needed to interpret older logs.
Centralized administration does not necessarily require identical physical readers. Different access systems can potentially participate in a common identity and audit framework through compatible integrations, synchronization services or documented mapping procedures.
Interoperability must be verified rather than assumed. Some existing devices may not support remote revocation, detailed event export or the synchronization behaviour needed for centralized control.
Once credential records are dependable, investigators must preserve the accompanying visual evidence without compromising its integrity.
The Export Mistakes That Can Compromise Security Video Evidence
Security video evidence can become difficult to use when exports omit source information, alter important visual details or lack a documented chain of custody. Common problems include inaccessible proprietary files, excessive compression, unexplained clipping and missing timestamps. A reliable export process preserves the original recording where possible and documents how every investigative copy was created, stored and transferred.
A video clip may appear persuasive during an initial security review but prove much less useful when an external investigator cannot open it or determine whether footage was removed.
Export quality should therefore be assessed before an incident, not when the organization is already responding to a legal or insurance request.
For systems using proprietary video formats, organizations should verify whether an appropriate viewer can be provided and whether a standard playable copy can be generated without losing essential information. The original source data should remain preserved where feasible.
A proprietary file is not automatically inadmissible evidence. The practical concern is whether authorized reviewers can access, authenticate and interpret its contents.
Investigators should also avoid treating an edited excerpt as the sole surviving record. Trimming may remove context, while heavy re-encoding can degrade details necessary to distinguish people, objects or actions.
Where a derivative clip is prepared, document the relationship between the original and edited files. Any enhancement or transformation should be identified rather than silently incorporated into a purported original.
A practical export record should identify the request, source system, camera, selected time interval, exporting operator, export time, output filename and destination storage location. It should also document transfers to subsequent custodians.
The NIST report on digital evidence preservation discusses digital evidence integrity, file provenance, cryptographic hashes and secure storage. These technical principles can guide Canadian facilities teams, although the report does not itself determine admissibility under Canadian law.
A cryptographic hash can help detect changes to an exported file after a documented reference hash was created. It cannot independently prove that the original camera recording was accurate, that the system clock was correct or that a person in the footage has been correctly identified.
When preserving a door-related incident, export the relevant access-control transactions along with the camera recording. Record the correlation method and any known timestamp discrepancies so subsequent reviewers can understand the relationship between them.
Finally, account for the retention race. Many video systems overwrite older recordings according to storage capacity and configuration. An organization should know the actual retention behaviour of each important camera and have a procedure for promptly preserving footage associated with a reported incident.
Reliable exports become more useful when one management environment can retrieve the associated access, alarm and operator records together.
Key Takeaways Before Choosing a Centralized Platform
- Require a demonstrable cross-site investigation workflow, not merely a dashboard that displays events from multiple buildings.
- Test integration quality, timestamp reliability and evidence portability using actual existing controllers and camera systems.
- Protect the central management layer with individual operator identities, restricted permissions and auditable administrative actions.
How a Centralized Security Management Interface Improves Multi-Site Operations
A centralized security management interface improves multi-site operations by allowing authorized teams to investigate access events, alarms, credentials and associated video from one coordinated environment. It reduces the need for separate manual queries at each building and provides a more consistent basis for monitoring and incident reconstruction. Its value depends on integration quality, operator controls and the reliability of underlying records.
For a Canadian organization managing buildings across several provinces, site-by-site investigation can require separate administrator accounts, different export formats and repeated communication with local teams.
A central interface can streamline that workflow by connecting site identifiers, credential records and relevant security events. An investigator could follow an assigned credential across locations without independently rebuilding its history in every local system.
However, centralization is not equivalent to evidence quality. If a controller fails to record denied entries, the central interface cannot reconstruct those missing events. If a camera and door controller have conflicting clocks, placing their records on the same screen does not automatically resolve the discrepancy.
The platform should therefore expose synchronization status, original event information, communication failures and integration limitations instead of hiding uncertainty behind a unified display.
During procurement or system evaluation, facility managers should conduct a practical investigation exercise involving more than one site.
| Capability | Required demonstration | Evidence to retain |
|---|---|---|
| Operator authentication | Individual accounts and supported single sign-on | Authentication configuration and test results |
| Role-based permissions | Restricted visibility and administrative actions by role | Permission matrix |
| Unified timeline | Correlated access, alarm and video records from multiple sites | Sample investigation timeline |
| Cross-site credential search | Historical events for a credential linked to a common identity | Reconciled event export |
| Evidence export | Retrievable records with provenance and integrity information | Test evidence package |
| Operator audit history | Traceable configuration changes, access and exports | Administrative audit report |
| Existing hardware integration | Verified support for selected installed controllers and readers | Compatibility test record |
Central management also changes staffing arrangements. A smaller security team may be able to oversee numerous locations remotely, provided alert routing, local intervention procedures and connectivity are adequately designed.
At the same time, a centralized environment concentrates sensitive security information and potentially powerful administrative permissions. Shared operator logins should be avoided because they make it difficult to attribute actions to a particular authorized person.
Individual accounts, least-privilege permissions and monitoring of configuration changes help maintain accountability. Exports should be logged, permissions periodically reviewed and privileged operations restricted to appropriate personnel.
The central interface is ultimately the point where consolidated access histories, alerts, synchronized timestamps, credential assignments and preserved evidence can become one coherent investigation process.
Its success should be measured through practical tests: whether a security team can identify relevant events, recognize missing data, retrieve corroborating footage and produce an understandable evidence package without compromising records or exposing unrelated personal information.
As a practical next step, select one representative security incident scenario, test the complete investigation from initial alert to evidence export across existing sites, and document every gap that needs remediation before expanding the system.
Can a badge access log prove that a particular employee entered a building?
Not by itself. A credential transaction establishes that the access system recorded activity associated with a credential. It does not necessarily establish who presented the credential or whether someone physically entered. Investigators should correlate the record with video, door-position information and other reliable evidence where available.
Should building security logs be encrypted?
Encryption is an important safeguard to consider for identifiable access records, particularly when they are transferred or stored centrally. Appropriate protection should also include access restrictions, authenticated administrative accounts, secure backups and monitoring. The exact safeguards should reflect the system architecture, sensitivity of the records and applicable privacy obligations.
How should security teams investigate a gap in access-control records?
First identify the affected controller, doors and time interval. Review communication failures, power events, local storage status and synchronization history. Preserve available alarm and video evidence, record the period of uncertainty and avoid interpreting absent transactions as proof that no entry occurred.
Can an organization investigate building access remotely from another Canadian province?
Remote investigation is technically possible when access systems support secure central retrieval and the organization has authorized the activity. Provincial differences in privacy law, employment context, system hosting and access permissions still require assessment. Centralized availability does not automatically authorize every operator to view all employee movement records.
What should a facility manager preserve immediately after discovering an unauthorized entry?
Preserve the relevant original access events, corresponding video, alarm history, credential assignment information and available controller health records. Record the incident timeframe, known clock discrepancies, exporting personnel and evidence storage locations. Escalate any potentially applicable preservation requirements before routine retention processes can remove relevant information.