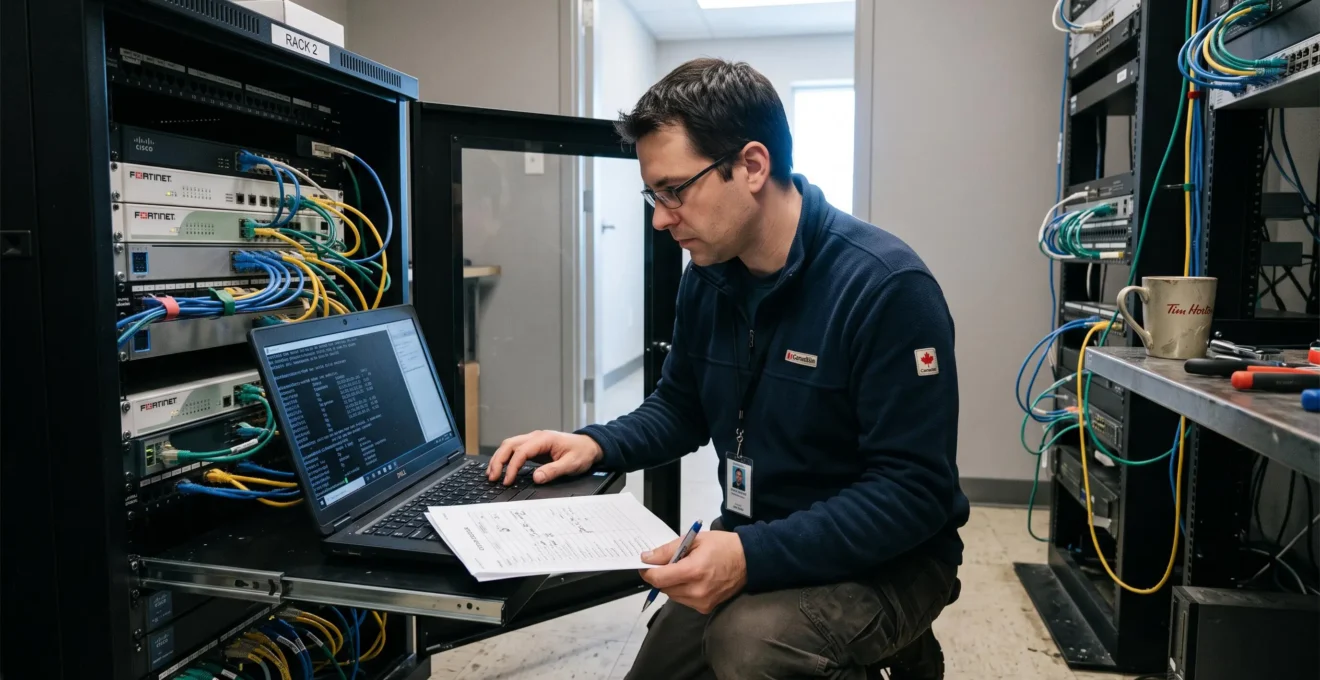
Encryption protects confidential business information only when it covers the places where data actually travels, resides and gets copied. For Canadian IT managers, the challenge is not simply enabling encryption. It is selecting safeguards that employees can use without losing access to essential systems, slowing business applications or creating unrecoverable data.
A practical approach starts with mapping sensitive information, identifying critical systems and choosing protections for each exposure. TLS can protect application connections, IPsec can secure communication between branches, and full-disk encryption can reduce the consequences of a stolen laptop. However, these controls depend on properly managed cryptographic keys, recoverable backups and tested configurations.
Canadian organizations also need to consider applicable privacy obligations, including federal PIPEDA requirements and Quebec’s privacy framework. Neither should be reduced to a universal mandate to purchase one particular encryption product.
The objective is a controlled deployment: protect the most consequential information first, verify recovery before expanding coverage, and maintain evidence that safeguards work.
Business encryption: the essential decisions
- Protect data according to its location and movement: TLS and VPNs for communications, disk and file encryption for stored information, and encrypted backups for recovery copies.
- Manage keys separately from the data they protect, with defined access, secure recovery and documented lifecycle decisions.
- Deploy in stages, beginning with critical assets, and test both connectivity and restoration before making changes organization-wide.
- Why Does Poor Encryption Key Management Expose Sensitive Data?
- How Can You Encrypt Data Connections Between Branch Offices?
- Full-Disk Encryption or File-Level Encryption for Employee Laptops?
- The Key Recovery Mistakes That Can Permanently Lock Business Data
- When Should Businesses Rotate Cryptographic Keys After Security Changes?
- Why Temporary Files Can Expose Data Despite Encrypted Primary Storage
- How Can Asset Criticality Determine Backup and Recovery Priorities?
- How Can Businesses Secure Data Both in Transit and At Rest?
Why Does Poor Encryption Key Management Expose Sensitive Data?
Poor encryption key management exposes sensitive data because encryption is only as effective as the protection of the keys used to decrypt it. A strong algorithm cannot prevent unauthorized access when an attacker obtains a valid key. Organizations therefore need to control key storage, access, inventory, recovery and retirement as carefully as the encrypted information itself.
Consider a database encrypted using a strong, appropriately implemented algorithm. If its decryption key sits in an application configuration file accessible to the same compromised account, the attacker may obtain both the ciphertext and the means to read it. The cryptography may remain mathematically sound while the confidentiality of the data is lost.
Other operational weaknesses include shared administrator credentials, keys embedded in application code, unnecessary access privileges and encryption secrets copied into spreadsheets or support tickets. Vendor-managed keys can also create an accountability gap when nobody has documented who controls them or how access is revoked.
Effective governance begins with an inventory that identifies each key’s purpose, protected system, custodian, storage location, access permissions and lifecycle status. Technical safeguards might include dedicated key management services, hardware security modules or suitably protected platform key stores, according to the organization’s risk and operational requirements.
The NIST SP 800-57 recommendations for cryptographic key management provide technical guidance on managing cryptographic keying material throughout its lifecycle. They are useful to Canadian IT teams but do not themselves establish Canadian legal obligations.
Weak key controls can become relevant to privacy incident assessments. Under PIPEDA, organizations subject to the legislation must report qualifying breaches involving a real risk of significant harm. Quebec’s framework separately establishes obligations concerning confidentiality incidents. A weak control alone does not automatically trigger notification; the facts and applicable threshold matter.
A useful management test is straightforward: can the IT team rapidly identify which systems hold decryption keys, who can access them and which keys need review? If the answer requires searching individual employee accounts, governance is already too dependent on undocumented knowledge.
Once key ownership is understood, the next question is where encrypted communications must travel and which network changes can be introduced safely.
How Can You Encrypt Data Connections Between Branch Offices?
Canadian organizations can encrypt connections between branch offices using site-to-site IPsec VPNs, encrypted SD-WAN configurations or encryption layered over private network circuits. The appropriate architecture depends on site count, application requirements, network reliability and operational capacity. A private telecommunications circuit should not be treated as encrypted simply because it is not directly exposed to the public internet.
Three architectures address different operational situations:
| Consideration | Site-to-site IPsec VPN | Encrypted SD-WAN | Private circuit with encryption |
|---|---|---|---|
| Typical use | Connecting a manageable number of locations | Coordinating multiple branches and network paths | Supporting dedicated connectivity requirements |
| Encryption | IPsec tunnel configuration | Encrypted overlays, depending on deployment | Additional encryption must be verified |
| Operational focus | Tunnel configuration and key negotiation | Central policy, routing and appliance management | Carrier responsibilities and encryption endpoints |
| Potential disruption | Tunnel drops during negotiation or configuration changes | Overlay or routing misconfiguration | Circuit or encryption equipment failure |
IPsec is a practical choice for many small and mid-sized networks, provided both endpoints agree on cryptographic settings, authentication, routing and rekeying behaviour. Configuration mismatches may prevent a tunnel from establishing or cause connectivity failures when security associations are renewed.
SD-WAN can simplify consistent policy management across numerous sites, but its encryption properties must be verified in the actual product configuration. Central management does not eliminate the need to validate tunnel establishment, administrative access and failover.
The Canadian Centre for Cyber Security’s system and communications protection controls identify TLS and IPsec as mechanisms for protecting information during transmission. The guidance also addresses cryptographic key management and encryption of stored information.
Before implementing inter-site tunnels, trace actual information flows. Staff may access cloud applications, remote desktops or third-party systems through routes that never pass through the branch VPN. Those connections require their own appropriate protections.
Operational validation should include connection monitoring, documented configuration baselines, failover exercises and a tested change-reversal procedure. Encryption can also reduce the visibility available to network monitoring tools, making endpoint telemetry and appropriate metadata monitoring important.
After securing links between locations, protect the devices that employees carry beyond those managed network boundaries.
Full-Disk Encryption or File-Level Encryption for Employee Laptops?
Full-disk encryption should generally provide the baseline protection for employee laptops because it protects stored information when a device is powered off and appropriately locked. File-level encryption addresses a different requirement: protecting selected documents independently of the device’s overall storage encryption. Organizations handling highly sensitive files may need both rather than choosing one exclusively.
Full-disk encryption protects the storage volume against many offline access scenarios, such as a stolen laptop or a drive removed from its computer. However, once an authorized operating system session has unlocked the volume, applications can access decrypted content according to their permissions.
File-level or container encryption can provide an additional boundary for sensitive documents, particularly when employees exchange files outside centrally managed environments. Its effectiveness still depends on secure key handling, access controls and the behaviour of applications that open decrypted files.
| Employee profile | Recommended approach | Primary consideration |
|---|---|---|
| Mobile and field employees | Managed full-disk encryption | Lost or stolen device exposure |
| General office staff | Managed full-disk encryption | Consistent endpoint protection |
| Legal, financial or health-record roles | Full-disk plus selective file or container encryption | Additional control of highly sensitive documents |
| Employees sharing confidential documents externally | Full-disk plus protected file-sharing mechanisms | Protection after files leave the device |
Built-in solutions such as BitLocker and FileVault can make encryption relatively unobtrusive after successful deployment. The rollout nevertheless requires attention to device compatibility, hardware-backed protection where applicable, centralized policy management and recovery key escrow.
Recovery material should be stored in an approved, access-controlled system independently of the laptop. Administrators should verify that the device reports successful encryption and that an authorized recovery procedure works before treating the deployment as complete.
A small pilot involving representative laptop models and employee roles helps reveal hardware limitations, authentication problems and applications that behave differently under new encryption policies. Expanding deployment only after those findings are resolved reduces helpdesk disruption.
Encryption also cannot replace endpoint security, screen locking or controlled user privileges. An attacker operating inside an unlocked session may still access files that the user or compromised process can read.
The next priority is ensuring that stronger laptop protection never creates an avoidable loss of access to essential business information.
The Key Recovery Mistakes That Can Permanently Lock Business Data
Business data can become permanently inaccessible when its only usable decryption key is lost, destroyed or controlled by someone who is unavailable. Common mistakes include keeping recovery credentials on the encrypted device, assigning custody to one administrator and never testing the recovery process. Reliable recovery requires protected, independent access to the necessary key material.
Imagine a hypothetical Canadian professional services firm whose sole encryption administrator leaves unexpectedly. The company’s storage remains operational, but no other employee can locate the required recovery credentials. If a hardware failure then requires rebuilding an encrypted system, valid backups may be unusable without the appropriate key.
This scenario illustrates the distinction between infrastructure availability and information recoverability. A functioning server or preserved backup does not guarantee that encrypted records can be restored.
A practical recovery governance design assigns at least two authorized custodians, establishes a documented escalation process and maintains recovery material outside the system it protects. Two custodians are a suggested organizational safeguard, not a universal statutory requirement.
Independent storage must also consider authentication dependencies. A recovery key stored in a vault that can be opened only through the failed identity system may be unavailable precisely when it is needed. Recovery arrangements should account for this failure path without creating unrestricted copies of sensitive secrets.
Canadian Centre for Cyber Security controls address maintaining information availability following key loss and identify key escrow as a recovery mechanism. An organization can translate that principle into documented custody arrangements and scheduled verification exercises.
A quarterly sample recovery test is one reasonable internal practice for critical environments, although the appropriate frequency depends on risk and operational requirements. Tests should prove that authorized personnel can retrieve the relevant material and restore access, not merely confirm that a file labelled “recovery key” exists.
Before selecting a cloud encryption or customer-managed key service, confirm the provider’s contractual and technical recovery responsibilities. Some services cannot decrypt customer information if customer-controlled keys are permanently lost.
Recovery planning provides the safety margin needed to manage cryptographic key changes without unexpectedly disabling production systems.
When Should Businesses Rotate Cryptographic Keys After Security Changes?
Businesses should review cryptographic keys for rotation when an event changes their exposure, trust or intended use. Relevant triggers include suspected compromise, loss of authorized custody, departure of personnel with key access and significant infrastructure or vendor changes. Periodic reviews remain useful, but no single calendar interval is appropriate for every key or cryptographic application.
The first distinction is between an event that requires investigation and one that requires immediate replacement. For example, an employee’s departure does not necessarily expose every organizational key. The response depends on which keys the employee could access, whether that access was exclusive and whether misuse or disclosure is suspected.
Key type also matters. Rotating a short-lived session key is operationally different from replacing a database encryption key that protects stored records. Some systems support changing a wrapping key without re-encrypting all underlying information, while others require more extensive migration.
An abrupt change can interrupt VPN tunnels, invalidate application credentials or make previously encrypted backups unreadable if old key versions are prematurely destroyed. Plan key transitions around application dependencies and recoverability.
A practical priority sequence is to assess compromised or exposed keys first, followed by keys protecting highly sensitive information or systems with extensive access. Lower-risk changes can follow a controlled schedule consistent with approved cryptographic policy.
Document each decision with the key identifier, affected assets, triggering event, approved action, planned change window and verification results. A rotation log also helps auditors distinguish a deliberate risk-based decision from an overlooked credential.
Five actions for a controlled encryption key rotation
- Identify the affected keys. Produce a register showing key identifiers, owners, protected systems and the reason for review.
- Map operational dependencies. Produce a list of applications, VPN endpoints, encrypted datasets and backups that require the keys.
- Verify recoverability. Record successful backup and recovery checks, including access to any key versions still needed for restoration.
- Execute a staged change. Produce an approved change record with deployment order, monitoring checks and a tested rollback or recovery strategy.
- Confirm and close. Save evidence of successful encryption and decryption tests, remove obsolete access and record whether previous keys can safely be retired.
The underlying principle is consistent with NIST key lifecycle guidance: cryptographic material needs controlled handling throughout its period of use, including when it is replaced or retired.
Even well-managed keys do not protect information that applications copy into locations outside the intended encryption boundary.
Why Temporary Files Can Expose Data Despite Encrypted Primary Storage
Temporary files can expose confidential information because applications may create additional copies outside the intended file-level or database encryption boundary. Autosave documents, print spools, cached attachments and exported reports may contain readable data. Full-disk encryption can protect these copies while the volume is locked, but it does not prevent access through an authorized, unlocked operating system session.
Consider an employee opening an encrypted document in an editing application. The application must normally access usable content to display and modify it. During that process, it may generate recovery files, previews or temporary working copies that do not inherit the document’s original encryption.
This is particularly relevant when a business relies on file-level encryption but assumes every derivative copy will remain protected automatically.
Locations worth examining include:
- Operating system temporary folders and application autosave directories.
- Downloaded email attachments and document preview caches.
- Local cloud synchronization folders and offline copies.
- Printer queues, spool files and document conversion workspaces.
- Removable drives, exports and backup staging directories.
Protection should combine multiple controls. Full-disk encryption provides a baseline for local storage at rest, while screen locking and access controls limit opportunities to use an active session. Sensitive applications may also need specific configuration for temporary storage, cache retention and file cleanup.
Data loss prevention policies can help detect or restrict sensitive information moving into unauthorized locations, but their coverage depends on the operating environment and configuration. Cleanup processes likewise require validation because deleting a visible temporary file does not necessarily guarantee that every underlying copy has been securely erased.
The same issue appears on servers. Database temporary tables, processing exports, replication destinations and backup staging areas may not share the encryption properties of primary data files.
An effective audit therefore follows information through processing and copying, not just through its primary storage location.
Understanding these secondary copies helps determine which assets and recovery environments require protection first.
How Can Asset Criticality Determine Backup and Recovery Priorities?
Asset criticality helps organizations prioritize encryption and recovery by identifying which systems would cause the greatest harm if their information became unavailable or exposed. IT teams should assess operational interruption, sensitive data, legal obligations and business dependencies. Critical systems generally deserve earlier protection, stronger recovery arrangements and more frequent restoration testing than assets with limited operational consequences.
A useful assessment considers the effects of losing access to each system for an hour, a day and a week. Impacts might include interrupted revenue, inability to serve customers, safety concerns or failure to meet contractual commitments.
The time horizons are assessment scenarios, not universal recovery objectives. They help business owners explain which interruptions are tolerable and which require immediate recovery capability.
| Asset category | Primary concern | Suggested protection priority |
|---|---|---|
| Essential transaction systems | Immediate business interruption | High: encryption, recoverable keys and early restore testing |
| Confidential customer records | Privacy and confidentiality impact | High: access controls, encryption and protected backups |
| Internal operational documents | Employee productivity and continuity | Risk-based: managed encryption and scheduled recovery validation |
| Low-use historical archives | Long-term confidentiality and retention | Phased deployment based on sensitivity and recovery requirements |
These are illustrative categories rather than fixed classifications. A rarely accessed archive containing highly sensitive personal information may warrant stronger confidentiality protection than a frequently used system with public data.
Encryption and backup policies must be developed together. An encrypted production database offers limited protection if its backups are exported without encryption. Conversely, an encrypted backup is of little recovery value when its decryption keys cannot be retrieved after a disaster.
For critical assets, consider suitably protected offline or immutable backup copies as part of ransomware resilience. Their usefulness still depends on correct implementation, administrative access separation and tested restoration procedures.
Restore exercises should verify the complete dependency chain: backup data, encryption keys, required infrastructure, application configuration and the authorized personnel able to perform recovery.
Prioritizing deployments also reduces operational disruption. Critical assets can enter a pilot and verification cycle first, while lower-priority systems follow after the organization has validated its encryption and recovery procedures.
Once those priorities are documented, the individual safeguards can be combined into a coordinated approach to protecting data throughout its lifecycle.
Key takeaways for implementation
- Inventory sensitive data flows before purchasing encryption tools; include endpoints, branch traffic, cloud services, temporary copies and backups.
- Choose encryption boundaries according to actual exposure, while keeping recovery credentials and administrative access under separate control.
- Make operational readiness measurable through staged changes, successful recovery tests and documented ownership of each protection.
How Can Businesses Secure Data Both in Transit and At Rest?
Businesses can protect data in transit and at rest by applying different encryption controls to each stage of information handling. TLS protects suitable application connections, IPsec can secure inter-site network traffic, and disk, file or database encryption protects stored information according to the threat model. Secure key management, encrypted backups and tested recovery make those controls operationally sustainable.
The most useful starting point is a data protection map. For every important category of information, document where it originates, which applications process it, where it travels, which devices store it and where secondary copies are retained.
A Canadian organization handling confidential client records might identify several distinct states:
| Data location or movement | Appropriate safeguard | Required operational check |
|---|---|---|
| Customer-facing websites and cloud connections | Properly configured TLS | Certificate validity, supported protocols and endpoint configuration |
| Traffic between branch offices | IPsec or suitably encrypted network overlay | Authentication, tunnel health, routing and failover |
| Employee laptops | Managed full-disk encryption | Device coverage and recovery key escrow |
| Highly sensitive files and database records | File, field or database encryption as appropriate | Access control, key separation and application compatibility |
| Temporary working data | Encrypted storage with suitable application and session controls | Cache locations and residual plaintext copies |
| Business backups and archives | Encrypted backup storage with independently recoverable keys | Restore success and recovery dependency testing |
This approach avoids treating encryption as one universal product. A TLS connection does not protect a downloaded file indefinitely, while full-disk encryption does not automatically secure an application session or a transmitted document.
Administrative controls must complement encryption. Identity management, least-privilege access, device security, logging and incident response remain important when authorized accounts or running systems are compromised.
In Canada, the legal assessment depends on the organization, its activities, the personal information involved and applicable jurisdiction. The Office of the Privacy Commissioner of Canada’s breach reporting guidance explains that organizations subject to PIPEDA must report qualifying breaches that create a real risk of significant harm, notify affected individuals when required and maintain breach records.
Quebec’s Law 25 framework separately requires the reporting of confidentiality incidents involving a risk of serious injury and maintenance of an incident register. Organizations should assess those requirements alongside their technical controls rather than assuming encryption automatically eliminates notification obligations.
A concise security record can capture what information is encrypted, which systems implement protection, who owns the keys, which parties can recover them and when the arrangements were last tested. This documentation supports incident analysis and discussions with auditors or cyber-insurers, although their specific requirements may differ.
For a low-disruption rollout, establish a representative pilot, verify recoverability, schedule changes around operational dependencies and monitor the protected services after deployment. Expand only when the technical and business owners have accepted the results.
Start with one critical information flow and document its storage locations, transmission paths, keys and recovery procedure. Validate the complete flow in a controlled deployment, then use the findings to extend encryption to the next priority asset without unnecessarily interrupting daily operations.
Is encryption mandatory for every Canadian business?
There is no single universal encryption product or configuration mandated for every Canadian business. Applicable privacy legislation and other sector-specific obligations must be assessed according to the organization and information involved. Encryption is an important potential safeguard, but its suitability depends on data sensitivity, threats and the broader security measures in place.
Does encrypted data automatically fall outside privacy breach reporting obligations?
No. Encryption may affect the likelihood that exposed information can be misused, but the circumstances still require assessment. Under PIPEDA, qualifying breaches are evaluated against the real risk of significant harm threshold. For Quebec’s private-sector framework, confidentiality incidents presenting a risk of serious injury have separate notification requirements. A compromised decryption key can materially change the assessment.
Can a company use cloud-managed encryption keys instead of operating its own key infrastructure?
Yes. Cloud-managed key services can reduce some infrastructure responsibilities, but the organization still needs to understand access policies, recovery arrangements, audit capabilities and vendor responsibilities. Customer-managed key configurations may create additional recovery obligations. The service agreement and technical documentation should establish what happens if credentials or key material are lost.
Will encryption slow down existing business applications?
Encryption introduces processing and administrative requirements, but the operational effect varies by device, workload, architecture and implementation. Modern hardware and managed encryption tools can reduce noticeable performance impact. Pilot testing should measure actual application behaviour, connectivity, startup processes and recovery operations before organization-wide deployment.
Should encryption keys be stored with encrypted backups?
Recovery keys should remain securely accessible without being exposed to the same compromise or failure as the protected backup data. Organizations should use separately controlled recovery arrangements, limit access to authorized custodians and test whether those arrangements work during an actual restoration exercise. Keeping the only recovery key inside the encrypted backup creates a potentially circular recovery dependency.