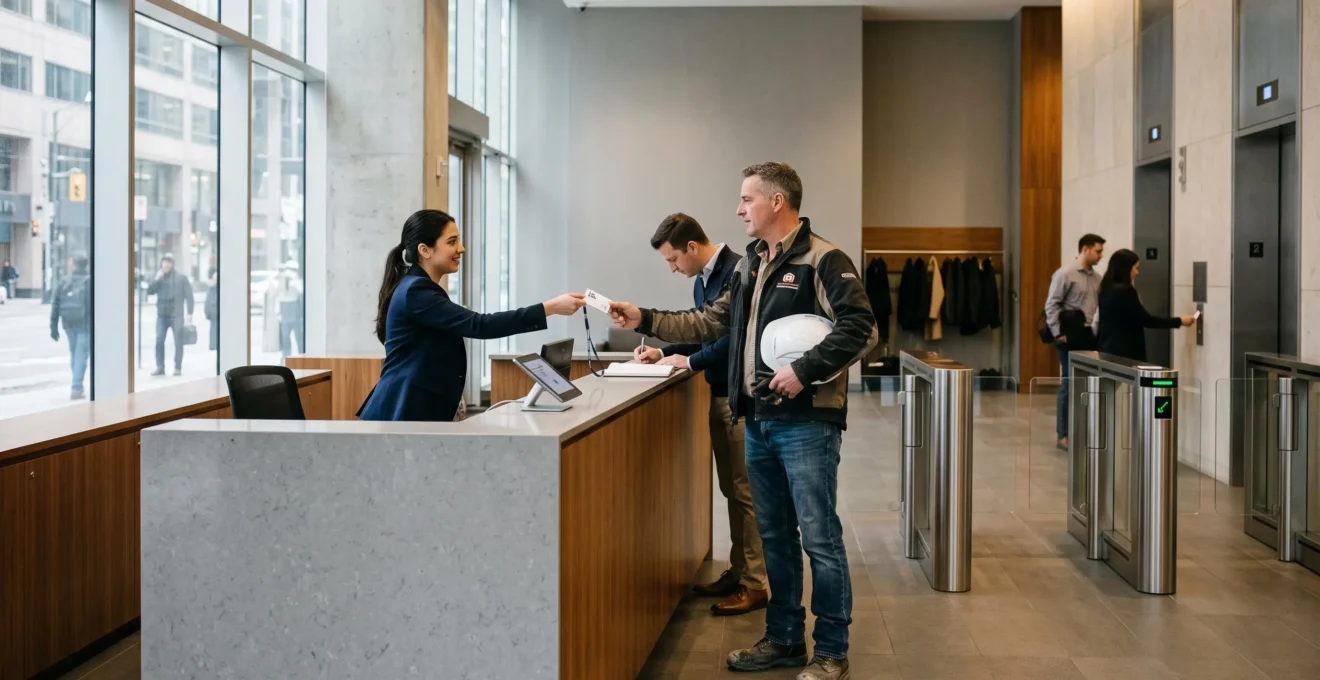
Canadian businesses can manage visitor and contractor access by establishing a consistent process for identity verification, entry authorization, credential issuance, movement restrictions, and departure tracking. The objective is straightforward: every person entering a controlled area should have a legitimate purpose, an accountable host or sponsor, and access privileges appropriate to their activities.
That becomes more complicated when a facility accommodates permanent employees, maintenance contractors, delivery drivers, consultants, and occasional guests. Each group requires different levels of verification and supervision. A visitor attending a meeting does not need the same permissions as a technician entering an equipment room, even when both arrive through the same reception desk.
Effective access governance combines physical controls with administrative procedures, workplace safety responsibilities, and reliable records. Canadian organizations must also consider the applicable federal, provincial, or territorial requirements, particularly when collecting personal information or controlling access to potentially hazardous workplaces.
Essential principles for controlling workplace entry
- Verify identity and purpose before granting access, then restrict each credential to authorized areas and periods.
- Pre-register contractors, coordinate access with safety approvals, and revoke credentials when assignments or responsibilities change.
- Maintain accountable entry records, establish incident-reporting procedures, and deploy new controls without compromising emergency exits or daily operations.
- Why Do Informal Visitor Sign-In Practices Increase Workplace Security Risks?
- How Can Facilities Track Contractors Without Delaying Maintenance Work?
- Escorted Access or Temporary Visitor Passes for Corporate Buildings?
- Why Shared Visitor Badges Create Accountability and Security Problems
- When Should Contractor Access Be Revoked After a Project Ends?
- How Can You Revoke Mobile Building Access When an Employee Changes Roles?
- How Should Security Officers Record Incidents During Overnight Shifts?
- How Can Canadian Businesses Implement Access Control Systems Without Disrupting Daily Operations?
Why Do Informal Visitor Sign-In Practices Increase Workplace Security Risks?
Informal visitor sign-in practices create security risks because recording a person’s name does not establish their identity, confirm their destination, or restrict their movement. A paper register may document an arrival without proving that access was authorized. Incomplete departure records also make it harder to identify who remains inside during an emergency or security investigation.
The distinction between registration and authorization is fundamental. A visitor who writes a name in a reception book has completed an administrative step, but the facility has not necessarily confirmed who they are, whom they are meeting, or which areas they may enter.
The RCMP GCPSG-006 Access Management Guide (2024) describes visitor registration, identity verification, access authorization, escorting, and personnel accounting as related security practices. Its recommendations are intended for Government of Canada facilities rather than automatically binding every private-sector business.
Facility managers can evaluate an existing register against four operational questions:
- Departure: Is the visitor’s exit recorded, or does the register only establish an arrival?
- Destination: Does the record identify the authorized area or meeting location?
- Accountability: Is an employee responsible for receiving and supervising the visitor?
- Identity: Has an appropriate verification process occurred, or is the name entirely self-declared?
These omissions matter during evacuations, investigations, and workplace safety reviews. For federally regulated workplaces, employer duties include safe workplace access and communicating known or foreseeable hazards to people who may encounter them, as explained in Employment and Social Development Canada‘s employer and employee duties guidance. Other Canadian workplaces are generally subject to their applicable provincial or territorial legislation. An incomplete register does not, by itself, establish a legal violation, but it can weaken the evidence available to demonstrate effective access supervision.
Paper registers can also expose personal information. An open book may reveal visitor names, employers, arrival times, and business relationships to people waiting at reception. For organizations subject to the federal privacy framework, the Office of the Privacy Commissioner of Canada‘s PIPEDA fair information principles explain requirements concerning collection purposes, limited collection, retention, and appropriate safeguards. Provincial privacy laws may apply instead or alongside PIPEDA.
A privacy-conscious visitor process should limit the information collected, prevent later visitors from seeing earlier entries, and apply an appropriate retention schedule.
Once identity, destination, and accountability are addressed, the next challenge is accommodating contractors whose work requires frequent entry without turning reception into an operational bottleneck.
How Can Facilities Track Contractors Without Delaying Maintenance Work?
Facilities can track contractors without unnecessarily delaying maintenance by completing eligibility checks before arrival and issuing access credentials against approved assignments. Pre-registration should confirm the contractor’s identity, sponsoring department, authorized work area, assignment period, and required safety documentation. Reception can then validate the arrival against an existing approval rather than reconstruct the entire authorization process at the entrance.
The principal distinction is between pre-accreditation and point-of-entry verification. Pre-accreditation gathers documents and confirms eligibility in advance. Entry verification checks that the person arriving matches the approved record and that the authorization remains valid.
Facilities should distinguish established maintenance providers from occasional contractors. A recurring service technician may qualify for a named credential with a defined validity period and approved zones. A contractor attending a single repair should generally receive more limited access associated with that particular assignment.
Building access must also remain distinct from authorization to perform hazardous work. Permission to enter a mechanical room does not automatically authorize confined-space entry, work at heights, or activities involving hazardous energy.
Canada’s federal confined-space regulatory guidance explains that relevant requirements extend to contractors and that employers retain responsibilities for applicable safety measures. It also clarifies that a formal entry-permit system is not universally required for every confined-space entry under the federal provisions; the applicable assessment and rules determine the requirements.
Where a work permit or equivalent approval is required, facilities can coordinate badge issuance with that approval while preserving the separate checks. This prevents a credential from being mistaken for a safety authorization.
An operationally useful measurement is the elapsed time between scheduled contractor arrival and actual work commencement. Track that interval alongside the reason for any delay, such as missing documentation, supervisor availability, incomplete safety approval, or reception processing.
The result should be an access process that supports maintenance scheduling while maintaining clear separation between permission to enter and permission to perform specific work.
Escorted Access or Temporary Visitor Passes for Corporate Buildings?
Corporate buildings should choose escorted access, temporary passes, or a combination based on the sensitivity of each area and the visitor’s authorization. Escorting provides direct supervision but consumes staff time, while temporary credentials can support independent movement within defined zones. Neither method should automatically grant unrestricted building access, and some areas may require both controls.
A practical decision begins by dividing the property into zones. Public reception areas, ordinary office floors, operational rooms, and spaces containing sensitive information have different exposure levels.
The following matrix illustrates a possible internal access policy rather than a universal Canadian legal requirement.
| Facility zone | Access approach | Operational condition |
|---|---|---|
| Public reception | Registration and host notification | No automatic access beyond the public area |
| General office area | Escorted visit or zone-limited temporary credential | Approved host, destination, and visit period |
| Technical or maintenance area | Restricted credential with supervision where required | Task authorization and applicable safety controls |
| Sensitive or designated security zone | Controlled access with escorting unless independently authorized | Relevant clearance, authorization, and local security policy |
Escorting has a less visible operational cost. The host must leave other duties, meet the visitor, supervise movement, and remain available until the visitor reaches an approved destination or departs. A policy requiring escorts is ineffective if visitors are routinely left unattended after initial check-in.
The distinction between a printed visitor pass and an electronic credential is equally important. A printed pass may identify its holder and display an expiry time, but it does not necessarily operate an electronic lock or prevent continued physical presence after expiry. An electronic card or mobile credential can enforce time and zone restrictions when supported and correctly configured.
Electronic credentials require defined expiry and revocation behaviour. For recurring consultants or business partners, a named, time-limited credential may offer a workable alternative to repeated daily registration or permanent escorting, provided the person has an approved sponsor and defined access scope.
Regardless of the method, authorization must remain attributable to the actual person using the credential. That requirement becomes difficult to enforce when visitor badges circulate informally between individuals.
Why Shared Visitor Badges Create Accountability and Security Problems
Shared visitor badges weaken security because access events become harder to attribute to a specific person. When several visitors use the same credential without a reliable issuance record, the system may show which badge opened a door but not who carried it. This reduces investigative value, complicates occupancy accounting, and can allow unauthorized individuals to enter controlled areas.
The risk is not simply that two people possess the same type of pass. It arises when a credential’s current holder cannot be established with confidence.
For example, consider a hypothetical contractor who returns a visitor badge to a reception counter, where another worker collects it without being registered. If the badge remains active, door records may identify the credential but cannot independently establish the second worker’s identity.
The consequences can extend to emergency response. Visitor registration and access logs can assist personnel accounting, but a badge count is not necessarily a person count. Badge transfers, tailgating, unrecorded exits, and people entering without using a reader can all undermine the accuracy of an occupancy estimate.
Shared or pooled credentials should not automatically be confused with prohibited employee credential sharing. The RCMP access-management guidance distinguishes individual identification credentials from visitor and contractor access cards that may be reassigned under controlled procedures. Its approach calls for effective control over the number and whereabouts of those cards.
For a private facility, the critical policy choice is whether reusable physical cards are allowed, and if so, how each assignment is associated with a verified person.
Corrective measures can include named badge issuance, sign-out and return reconciliation, immediate deactivation of missing cards, and contractual requirements preventing unauthorized credential transfers. Systems capable of detecting conflicting or anomalous credential use can provide additional alerts, although such alerts do not independently prove which individual used the card.
Reception delays and cumbersome reissuance procedures are also worth examining. If obtaining an authorized badge is difficult, people may develop informal sharing practices to keep work moving.
Reliable attribution depends on controlling both credential assignment and its useful lifespan. Once a contractor’s assignment finishes, continuing access creates a different form of accountability gap.
When Should Contractor Access Be Revoked After a Project Ends?
Contractor access should be revoked when the business justification for that access ends, not merely when someone remembers to collect a badge. Project completion, early termination, personnel reassignment, and the end of an approved warranty visit can each trigger different changes. Facilities should establish these triggers before granting access and avoid leaving credentials active without a current sponsor or assignment.
A single company-wide revocation date is unlikely to accommodate every engagement. A construction subcontractor finishing an installation has different needs from a service provider retained for scheduled follow-up maintenance.
Facilities can use a trigger-based policy:
| Trigger | Physical access action | Administrative follow-up |
|---|---|---|
| Contract or assignment completed | Disable access no longer justified by the completed work | Confirm closure with the project sponsor |
| Warranty or follow-up work approved | Issue separately scoped access for the authorized visit | Record the new purpose and expiry |
| Individual contractor leaves the project | Revoke that individual’s credentials | Update the contractor personnel roster |
| Contract terminated early | Apply the termination-related access controls promptly | Coordinate with procurement, security, and the contract owner |
Physical access is only one part of offboarding. A contractor may also retain building keys, shared entry codes, visitor-management accounts, maintenance software permissions, remote support connections, or access to project documentation.
Digital and physical entitlements should be reviewed together. Collecting a badge does not disable an application account, and terminating a remote maintenance login does not invalidate a mechanical key.
Residual privileges become more difficult to justify when the underlying work is no longer active. They can also create uncertainty during subsequent security investigations because the facility may no longer have a clear reason for an access event.
As an internal governance measure, a quarterly comparison of active contractor credentials against current projects can help identify orphaned access. This is a suggested review cadence, not a universal Canadian regulatory deadline.
Five actions for auditable contractor offboarding
- Confirm the contractor’s assignment status with its internal sponsor and retain a dated closure confirmation.
- Export all active physical credentials associated with the contractor and produce a credential reconciliation record.
- Revoke unnecessary badges, mobile credentials, keys, and codes, documenting their disablement or recovery.
- Review associated software accounts and remote connections, maintaining an access-removal confirmation for each applicable system.
- Compare the final offboarding record with the active-access inventory and document any justified exceptions with an owner and expiry date.
The same principle applies to permanent employees: access should follow current responsibilities, not accumulate indefinitely as people move between roles and facilities.
How Can You Revoke Mobile Building Access When an Employee Changes Roles?
Mobile building access should be updated when an employee’s responsibilities change by removing permissions associated with the previous role and granting only those required for the new one. Where supported, an approved human resources event can trigger an identity and access-management workflow. Security teams must also verify that revoked privileges are no longer accepted by relevant door controllers.
Role changes require more precise handling than a simple active-or-inactive employment status. An internal transfer may preserve ordinary building entry while removing access to a former department. A promotion can require additional permissions, while extended leave or permanent departure may justify suspension or broader revocation under applicable policies.
A role-based access model associates permissions with defined responsibilities. When an employee changes departments, the process should calculate the permissions of the new role rather than simply adding them to everything already granted.
This helps limit privilege creep, the gradual accumulation of permissions that remain available after their original justification disappears.
Mobile credentials introduce additional technical questions. Some access-control architectures involve offline readers, locally stored permissions, or credentials that function without continuous communication. Their actual revocation behaviour depends on the system’s design and configuration.
A facility should therefore ask its provider how revocation is propagated, how disconnected devices or readers are handled, and whether cached authorization can remain usable for any period. Immediate revocation should not be assumed without testing the specific deployment.
Cross-site assignments also require special treatment. An employee whose primary role changes may still need legitimate access to another facility for a temporary project. Such access can be managed as a separately approved, time-limited entitlement rather than remaining attached indefinitely to a former job title.
The operational record should identify the triggering HR event, old and new permission sets, approving authority, effective date, and verification result.
Even a well-maintained authorization system needs monitoring. Outside normal business hours, the quality of security incident records becomes particularly important when unexpected access activity occurs.
How Should Security Officers Record Incidents During Overnight Shifts?
Security officers should document overnight incidents promptly using consistent timestamps, observable facts, relevant system records, and clear descriptions of actions taken. Automated access events should be distinguished from an officer’s written account. Reports should identify unresolved issues and support an explicit shift handover, especially when staffing levels and supervisory availability are limited.
Overnight operations can involve fewer witnesses, reduced immediate support, and fatigue-related reporting challenges. A structured incident template helps prevent essential details from being overlooked during a demanding shift.
The distinction between a system event and an incident report is important. A door controller may record a denied credential at a particular time, but that event does not, by itself, establish attempted intrusion or malicious intent.
The officer’s report should document what was actually observed, including the access point, credential event, persons seen where reasonably identifiable, actions taken, and subsequent notifications.
For example, an appropriate factual entry would describe that a particular door reader recorded repeated denials and that the officer subsequently checked the area. It should not claim that an identified individual attempted a break-in unless evidence supports that conclusion.
Where relevant, preserve associated access logs, camera references, radio communications, and report identifiers under the organization’s evidence-handling and retention policies. Records should distinguish original observations from later findings or corrections.
Shift handover should make unresolved conditions visible to the incoming team. A useful status vocabulary is open, escalated, and closed, with an assigned follow-up owner wherever action remains outstanding.
Repeated overnight anomalies deserve particular attention. Several individually minor denied entries or door-held-open alerts may be operationally significant when reviewed together, even when each event required little immediate intervention.
The reporting process should also account for applicable occupational health and safety incident-recording obligations and the organization’s incident escalation requirements.
Incident records can then inform access-policy changes and system improvements. Those improvements, however, need to be introduced without creating avoidable disruption for employees and authorized visitors.
Key takeaways before implementing new access controls
- Define who owns authorization decisions before selecting readers, badges, or visitor-management software.
- Test the entire entry journey, including contractors, deliveries, emergency procedures, and exceptions, rather than focusing only on employee access.
- Use actual entry records, user feedback, and unresolved incidents to determine whether a rollout is functioning as intended.
How Can Canadian Businesses Implement Access Control Systems Without Disrupting Daily Operations?
Canadian businesses can implement access control systems with less disruption by introducing them in phases, validating essential entry routes, and providing supervised fallback procedures during transition. The rollout should involve facilities, security, IT, workplace safety representatives, and relevant property stakeholders. Each phase needs clear acceptance criteria covering authorization accuracy, reception capacity, emergency egress, and continued access for legitimate work.
A phased deployment is generally easier to troubleshoot than switching every building and user group simultaneously. Start by documenting existing access points, user categories, delivery routes, and current authorization procedures.
Then pilot the proposed workflow in a defined area or with a controlled user group. During an appropriate transition period, the previous process may remain available under supervision while the new system is validated. Parallel operation should not mean leaving uncontrolled entry routes permanently open.
Peak-hour reception demand is a practical concern. Employee arrivals, scheduled visitors, deliveries, and maintenance teams may converge at the same entrance. Testing should include these circumstances rather than only low-traffic operating periods.
Emergency egress must be treated as a design constraint. Access-controlled doors, electric locking arrangements, and related hardware must be evaluated against the applicable building and fire requirements. Canadian building-code adoption and enforcement depend on the relevant jurisdiction, and security restrictions cannot simply override required emergency exit provisions.
Ownership responsibilities also influence deployment. In leased premises, a tenant may not have unilateral authority to modify shared entrances, fire doors, or building infrastructure. Multi-tenant facilities require coordination between the property owner, building manager, affected tenants, and system administrators.
Where applicable, health and safety representatives or committees should be involved in assessing changes that affect workplace access and evacuation arrangements.
Training should be adapted to the user group. Employees need to understand credential use and access exceptions. Reception personnel require issuance and escalation procedures. Contractors need advance instructions covering arrival, work authorizations, and returning credentials. Delivery drivers may need a separate route or supervised receiving procedure.
The initial operating period should include additional reception support where necessary, accessible instructions, and a documented channel for reporting access failures. Repeated exceptions can identify incorrectly configured permissions or unrealistic procedures.
Before expanding the rollout, managers should review denied entries, unauthorized access attempts, onboarding delays, missing credentials, emergency-exit testing results, and user-reported obstacles. Any system changes should be documented and retested.
The practical next step is to map each facility’s entry points, authorized user groups, responsible approvers, and existing control gaps, then select a limited pilot area with measurable security and operational acceptance criteria before broader deployment.
Do Canadian businesses have to check government-issued identification for every visitor?
There is no universal requirement established by the referenced Canadian guidance for every private business to inspect government-issued identification for every visitor. Verification practices should reflect applicable law, facility risk, contractual requirements, and organizational policy. Government facility guidance may recommend stricter procedures without automatically imposing them on private workplaces.
How long should a company retain visitor registration records?
There is no single retention period established by the referenced sources for all Canadian visitor logs. Organizations should define a documented period based on legitimate operational needs, applicable privacy legislation, legal obligations, and any relevant retention requirements. Records should not be kept indefinitely without justification.
Can a visitor management system replace workplace safety orientation?
No. Visitor management can support registration, identity checks, and access authorization, but it does not independently satisfy applicable workplace safety responsibilities. Contractors and other entrants may require hazard information, protective equipment, training, supervision, or specific work authorization depending on the activities and applicable regulations.
Should delivery drivers receive the same access permissions as maintenance contractors?
Not ordinarily. Delivery drivers can often be directed to receiving areas or supervised unloading locations, while maintenance contractors may require specific technical-zone access. Each group’s authorization should correspond to its actual task, location, and duration, subject to facility policy and safety requirements.
What should a facility do if its electronic access system becomes unavailable?
Facilities should maintain a documented contingency procedure identifying which authorized personnel can verify entrants, how temporary entry decisions are recorded, and when normal controls must be restored. Any fallback must preserve required life-safety functions and avoid creating unrestricted access. Recovery procedures should include reconciling temporary entries and privileges after service returns.