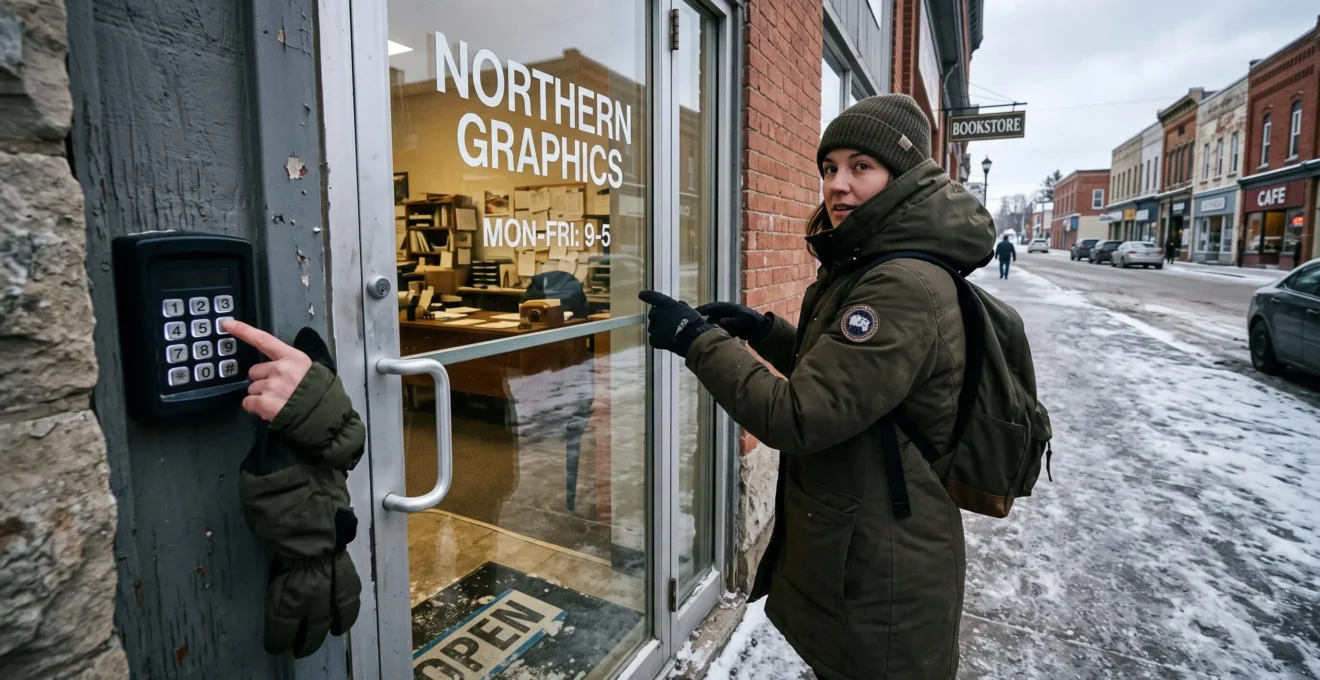
Numerical PIN-controlled doors offer Canadian businesses a convenient way to manage building access, but their security depends on more than the quality of the keypad itself. A code shared among employees, contractors and cleaning staff can gradually become an uncontrolled access credential, particularly when nobody maintains a record of who knows it.
Strengthening keypad authentication means controlling who receives each PIN, limiting how credentials are shared, and establishing a reliable process for changing or revoking access. Businesses must also consider how people enter codes in public-facing areas, whether their hardware supports individual user profiles, and whether physical entry permissions match employees’ actual responsibilities.
The most practical approach combines individual credentials where accountability matters, controlled shared access where operationally justified, and regular reviews of active permissions. Canadian government security guidance provides useful reference points for these practices, although its recommendations should not automatically be interpreted as legal requirements for private businesses.
Key Principles for Securing Commercial Keypad Doors
- Replace uncontrolled shared PINs with individual credentials wherever accountability and access tracking are important.
- Change compromised codes promptly and communicate new credentials through controlled, individual channels.
- Maintain an access register covering employees, contractors, permissions, credential changes and revocations.
- Why Are Reused Four-Digit Door Codes Vulnerable to Unauthorized Access?
- How Can You Rotate Door PINs Without Locking Out Authorized Staff?
- Individual PINs or Shared Entry Codes for Small Commercial Teams?
- Why Shoulder Surfing Remains a Risk at Public-Facing Keypads
- When Should a Door PIN Be Changed After Employee Departure?
- Why Do Former Employees Sometimes Retain Active Building Credentials?
- Electric Strikes or Magnetic Locks for Commercial Entry Doors?
- How Can Canadian Organizations Structure Access Permissions by Employee Role?
Why Are Reused Four-Digit Door Codes Vulnerable to Unauthorized Access?
Reused four-digit door codes become vulnerable when too many people know them and the business cannot identify who still has access. A shared PIN may initially be distributed to a small team, but contractors, cleaners, temporary workers and former employees can gradually expand its circulation. The principal weakness is therefore not simply the number of digits: it is the loss of control over credential ownership and distribution.
A four-digit PIN has a theoretical combination space of 10,000 possibilities, from 0000 to 9999. However, this does not mean every code offers equivalent practical protection. Common choices such as birth years, repeated digits and ascending sequences make some combinations easier to anticipate than others. A keypad without appropriate lockout or anti-tampering protections may also provide fewer obstacles to repeated guessing.
There are two distinct security problems to identify:
- Compromised credentials: Someone unauthorized has learned or obtained the code. The PIN should be treated as exposed and changed promptly.
- Overdistributed credentials: Too many authorized and potentially unauthorized individuals know the code. Changing it without controlling its redistribution simply recreates the same problem.
The Royal Canadian Mounted Police identifies generic and shared keypad codes, guessed combinations and codes observed by unauthorized individuals as access-control vulnerabilities. Its RCMP Access Management Guide (GCPSG-006) recommends individual PINs for staff and scramble keypads to reduce the likelihood of observers memorizing entered codes.
For Canadian small businesses, inherited credentials deserve particular attention. A company moving into an existing commercial unit may receive a keypad code that predates its tenancy. Previous tenants, property managers, maintenance contractors or other third parties may still know it.
The first security review should therefore establish whether the current PIN was created specifically for the business, who received it, and whether its previous distribution can be established. If its history is unknown, replacing it is a sensible starting point.
Restricting code distribution also requires an operational rule: every person receiving a credential should have a defined access purpose and an identifiable period of authorization. This principle becomes especially important when deciding how frequently a PIN should be changed.
A new combination can eliminate an exposed credential, but it cannot prevent future overdistribution on its own. Effective protection requires a process that controls who receives the replacement code and when their authorization ends.
How Can You Rotate Door PINs Without Locking Out Authorized Staff?
Canadian businesses can rotate door PINs without disrupting authorized access by planning the change, programming the replacement credentials and verifying entry before retiring the previous configuration. The process should account for every keypad, user group and secondary credential, rather than treating the main entrance code as the only access point that matters.
A controlled rotation can follow three operational phases.
Phase 1: Announce the change window. Identify the employees, contractors and other authorized users who need access during the transition. Communicate the planned timing and establish who will administer the keypad. Employees working outside normal business hours should have an alternative access arrangement if the programming process temporarily interrupts entry.
Phase 2: Reprogram outside operating hours. Where practical, schedule the change when fewer people depend on the entrance. Configure the replacement PIN or individual user credentials and check that the relevant access permissions remain intact.
Phase 3: Verify access before completing the transition. Test the new configuration on every affected keypad. Confirm that authorized users and relevant user categories can enter before deactivating the previous credential, provided the system supports this sequence. If the controller cannot maintain both configurations temporarily, arrange an alternative authorized entry method.
The frequency of rotation should reflect actual exposure rather than an arbitrary calendar rule. Consider these factors:
- Team size: A shared code known by a small, stable team has a different exposure profile from one distributed across numerous departments.
- Staff turnover: Frequent employee departures create more opportunities for credentials to remain in circulation.
- Credential structure: Individual PINs allow specific accounts to be revoked without necessarily changing everybody else’s credentials.
- Security incidents: Suspected disclosure or unauthorized observation calls for a risk-based response rather than waiting for a scheduled review.
Another important consideration is how the replacement code is distributed. Sending it through the same group chat, shared document or publicly visible notice used for the old code can undermine the entire exercise.
Use individual delivery wherever possible, restrict access to credential records and avoid writing a PIN alongside the door or location it controls. Also verify whether changing a master credential affects secondary user codes: controller behaviour varies, and some systems may reset or desynchronize other programmed credentials.
Every rotation should produce a simple record containing the date, affected access points, responsible administrator and verification outcome. This creates an operational history that makes subsequent reviews more reliable.
Rotation should ultimately reduce exposure without creating unnecessary access interruptions. The right frequency and workflow depend on the business’s staffing pattern, system capabilities and ability to manage credentials individually.
Individual PINs or Shared Entry Codes for Small Commercial Teams?
Individual PINs generally provide better accountability because each credential can be associated with a specific employee, while shared codes are simpler to administer for small, stable teams. The appropriate choice depends on the business’s security requirements, staff turnover, keypad capabilities and need to investigate who entered a building at a particular time.
Three practical criteria help determine which arrangement makes sense.
1. System cost and technical capability
A shared-code arrangement can work with a relatively simple keypad. Individual PINs require a controller capable of storing and managing multiple user credentials. Before upgrading, check the manufacturer’s specifications for the maximum number of users, credential deletion, access schedules and event-recording capabilities.
2. Accountability and entry records
Individual credentials make it easier to associate recorded access events with specific users. The RCMP recommends assigning individual PINs to staff, while its guidance on electronic access systems describes recording where entry occurred and which key or device was used.
Shared codes provide less attribution. If an incident occurs, several people may have had access through the same credential, making internal investigations and after-hours access reviews more difficult.
3. Administration and staff turnover
Individual credentials require administrators to create, modify and revoke user access whenever staffing arrangements change. Shared codes reduce some administrative work, but each departure or suspected disclosure may require a wider credential change and redistribution exercise.
The following comparison helps identify the operational trade-offs.
| Criterion | Individual PINs | Shared entry codes |
|---|---|---|
| Accountability | Supports user-specific access attribution when logs are available. | Does not reliably identify which individual used the code. |
| Administration | Requires individual credential management. | Usually simpler for a small authorized group. |
| Employee departures | Specific credentials can be revoked. | May require changing and redistributing the shared code. |
| System requirements | Requires multi-user programming capabilities. | Can work with simpler keypad configurations. |
| Access monitoring | Can support individual entry records on compatible systems. | Provides limited user-level attribution. |
For a small business with a few trusted employees, low turnover and limited after-hours access requirements, a shared code may be an acceptable operational compromise. Individual PINs become more valuable when management needs to determine who entered and when, particularly after an incident or when access records support insurance or workplace documentation.
A hybrid arrangement can also work well. Permanent employees receive individual credentials, while cleaners, delivery personnel and temporary contractors receive a separate shared or time-limited credential where the controller supports it. This keeps third-party access separate from the main employee credential system.
Canadian businesses should also consider the consequences of incomplete access records. A shared PIN may establish that someone entered through an authorized credential, but it does not necessarily establish who that person was.
When individual credentials are technically and financially practical, they provide a stronger foundation for managing employee departures, contractor access and security investigations. The next consideration is protecting those credentials from observation at the entrance itself.
Why Shoulder Surfing Remains a Risk at Public-Facing Keypads
Shoulder surfing remains a risk because someone standing near a commercial entrance may observe a PIN while an authorized person enters it. The code can be captured directly, recorded on a phone or inferred from frequently used keypad buttons. Public-facing entrances therefore require attention to both the physical visibility of the keypad and the behaviour of people using it.
Direct observation is the most obvious threat. A customer, delivery driver or passerby may be positioned close enough to see the employee’s hand movements. Even when the user attempts to shield the keypad, the viewing angle may allow someone nearby to reconstruct the sequence.
Recording devices introduce another exposure. A phone camera positioned near a reception area, neighbouring storefront or delivery entrance may capture repeated entry sequences without attracting immediate attention.
Physical wear can provide an additional clue. If the same four keys are used repeatedly on a numerical keypad, those buttons may become more polished or visibly worn than others. This does not necessarily reveal the complete code, but it can reduce the uncertainty surrounding frequently used combinations.
Several practical controls can reduce these risks:
- Review keypad positioning: Avoid placing the device directly within the sightline of public waiting areas, neighbouring entrances or street-facing windows where installation constraints allow.
- Use privacy-conscious hardware: Consider scramble keypads or other observer-resistant designs supported by the access-control system.
- Train employees: Encourage users to shield their PIN entry and check whether unfamiliar people are positioned to observe the process.
- Inspect physical wear: Include keypad condition and visibility in routine entrance security checks.
- Respond to suspected observation: Treat an observed or recorded code as potentially compromised and assess whether it needs immediate replacement.
The RCMP specifically recommends scramble keypads as a measure to make it harder for unauthorized observers to memorize entered PINs. Such features are not available on every system, so compatibility should be checked before purchasing replacement equipment.
Businesses should also evaluate the surroundings rather than inspecting the keypad in isolation. A practical assessment involves viewing the entrance from the street, parking area, delivery approach and neighbouring commercial units.
Shoulder surfing can reveal more than a numerical combination. An observer may also learn when employees arrive, which entrance they use and how frequently the building is accessed. This additional operational information can make a compromised credential more useful to someone attempting unauthorized entry.
Improving visibility and user behaviour reduces opportunities for observation, but it cannot replace credential management. If someone has already seen a PIN, the business must address the compromised credential rather than relying exclusively on better shielding practices.
When Should a Door PIN Be Changed After Employee Departure?
A door PIN should be changed or revoked when an employee no longer has authorization to use it, particularly when the credential is individual, shared with other people or potentially retained outside the business. Employee departure is one of several access-control triggers, alongside contractor contract expiry, suspected disclosure, lost devices containing credentials and changes to cleaning or maintenance arrangements.
The appropriate response depends on how the keypad is configured.
With individual PINs, the preferred approach is to deactivate the departing employee’s credential without unnecessarily affecting the rest of the team. This reduces disruption and preserves other users’ access permissions.
With shared codes, the departure creates a more complicated situation. If the employee knew the common entrance code, the organization must decide whether the credential remains sufficiently controlled. Where continued access cannot be justified, changing the shared PIN is a prudent measure.
A practical departure process should cover several actions:
- Identify the employee’s physical access credentials before the departure takes effect.
- Arrange for individual PIN deactivation or shared-code replacement according to the system configuration and risk.
- Recover physical keys, cards and other access devices issued by the organization.
- Check whether access codes were stored on company equipment, personal devices or shared notes.
- Verify the updated access configuration and retain a record of the credential change.
For an involuntary or contentious departure, access arrangements may need to be addressed before the employee is informed, where legally and operationally appropriate. A business should coordinate the timing with its HR and security procedures rather than leaving a preventable period during which a departing person retains access.
Canadian Centre for Cyber Security guidance states that physical access authorizations should be maintained and individuals removed when access is no longer required. It also recognizes changes in employment status as a reason to remove physical access credentials.
Where the system maintains event records, administrators can review relevant entries after revocation, including repeated attempts to use an inactive credential. Such records may help identify access-control issues, although a failed attempt alone does not establish who made it.
The Canadian Centre for Cyber Security physical access controls provide a useful framework for maintaining authorized access lists, reviewing permissions and removing credentials when access is no longer required.
Prompt revocation is only effective when the organization knows which credentials the employee held. This leads to a broader governance issue: former employees can sometimes retain building access through credentials that nobody realizes are still active.
Why Do Former Employees Sometimes Retain Active Building Credentials?
Former employees sometimes retain building access because physical credentials are managed separately from employment records and digital accounts. An organization may deactivate a person’s email and software accounts while overlooking an individual PIN, shared entrance code, contractor badge or physical key. Without a clear owner for physical access management, these credentials can remain active after employment ends.
Several organizational weaknesses contribute to this problem.
Decentralized onboarding and offboarding can leave access management fragmented. HR may notify IT about a departure, but nobody may inform the person responsible for programming the entrance keypad. The result is an employee who has lost digital access but may still be able to enter the premises.
Multi-site operations introduce another complication. Each branch may maintain its own access codes and administrator. If the departure process is centralized but physical credential management remains local, one or more sites may fail to revoke access.
Third-party access arrangements can also preserve indirect entry opportunities. A former employee may know a shared PIN used by current staff, retain a contractor credential, or have access to a master code controlled by a landlord or property manager.
This is why an access review must consider more than credentials directly assigned to the departing employee. It should identify every route through which that person could still enter the building.
Canadian government biosecurity guidance provides a useful example of structured credential governance. The Public Health Agency of Canada and Canadian Food Inspection Agency recommend processes for granting, modifying and removing access when personnel resign or are terminated. Their guidance also addresses credential sharing, recordkeeping and access for cleaning and maintenance personnel.
Although this publication focuses on biosecurity facilities rather than ordinary commercial premises, its recordkeeping principles offer useful reference points for organizations seeking better physical access controls.
A practical reconciliation process compares the current employee and contractor lists with the credentials programmed into each keypad and other access-control device. Every active credential should have an identifiable holder, an authorized purpose and a current status.
Any credential that cannot be matched to a current authorized person should be investigated and, where authorization cannot be established, deactivated. A quarterly reconciliation can be an operational choice for businesses seeking a recurring review cycle, but it is not a universal interval prescribed by the cited Canadian guidance.
Useful access records should contain:
- The name of the person receiving the credential.
- The type of credential and the entrance or zone it controls.
- The date the credential was issued.
- The date authorization was modified or revoked.
- The person responsible for administering the change.
Maintaining this information also helps demonstrate that access permissions are actively managed. It can support internal investigations and the documentation of after-hours incidents, although the existence of an access register does not by itself establish compliance with every applicable legal or insurance obligation.
Once an organization can reliably identify active credentials, it becomes easier to align access rights with actual responsibilities. That requires considering not only who can enter the building but also how the locking hardware behaves during normal operation and emergencies.
Key Decisions Before Choosing Commercial Door Hardware
- Confirm whether the door is primarily an entry-control point or part of an emergency exit route.
- Check how the selected locking mechanism behaves during power failure and fire-alarm activation.
- Verify compatibility with the applicable provincial or territorial building and fire requirements before installation.
Electric Strikes or Magnetic Locks for Commercial Entry Doors?
Electric strikes and magnetic locks both support electronically controlled commercial entry, but they use different locking mechanisms and have different installation and emergency-release considerations. An electric strike controls the door’s latch at the frame, while a magnetic lock holds the door using electromagnetic force. The appropriate choice depends on door construction, access-control requirements and the applicable emergency-egress rules.
Understanding how each mechanism works helps businesses avoid choosing hardware based solely on convenience or perceived strength.
Electric strikes are installed in the door frame and release the strike mechanism to allow the door latch to move when authorized access is granted. They can be suitable for entrances where a numerical keypad controls the release of a conventional latched door.
Magnetic locks use an electromagnetic holding mechanism, typically mounted across the door and frame. When electrical current is removed from the locking mechanism, the magnetic holding force is released.
The Royal Canadian Mounted Police explains these fundamental hardware differences in its access management guidance. However, the specific behaviour of an installed electric strike during power loss depends on its design and configuration. Businesses should not assume that every strike automatically remains locked when electrical power fails.
The main purchasing considerations include:
| Criterion | Electric strike | Magnetic lock |
|---|---|---|
| Locking mechanism | Controls the door-frame strike and latch interaction. | Uses electromagnetic force to hold the door closed. |
| Power-loss behaviour | Depends on the strike’s fail-safe or fail-secure design. | Releases when electrical current to the magnet is removed. |
| Door compatibility | Depends on latch type, frame construction and strike dimensions. | Requires suitable mounting and contact between the magnetic components. |
| Access integration | Can release a compatible latch following authorized keypad input. | Can integrate with access controllers and authorized release systems. |
| Emergency egress | Must be configured to meet applicable exit-door requirements. | Must satisfy applicable emergency-release and fire-safety conditions. |
Emergency egress is particularly important in Canada. The National Building Code of Canada 2020 includes provisions governing exit-door hardware, including requirements concerning opening from the inside without keys, special devices or specialized knowledge, subject to specified exceptions.
For certain electromagnetic-lock configurations, the Code establishes conditions involving release through the building fire-alarm system and immediate release following loss of power controlling the locking mechanism and associated auxiliary controls.
The National Building Code of Canada 2020 is a model code. Its provisions become applicable legal requirements through adoption by provincial or territorial authorities, potentially with local amendments. Businesses must therefore verify the applicable jurisdictional requirements and the specific door configuration rather than assume one universal rule applies to every commercial entrance.
In practical terms, magnetic locks may suit controlled entrances that need electronic release through reception or a buzzer system. Electric strikes may be appropriate where an existing latch arrangement can be retained and the keypad is the principal authorization mechanism. Neither choice should be made without assessing the exit route, hardware specifications and installation conditions.
Hardware improvements should be integrated with the credential-management practices discussed earlier. An advanced locking mechanism cannot compensate for an entrance code that is widely shared, poorly documented or still known by former employees.
The most effective installation combines suitable locking hardware, a compatible access controller and a clearly managed authorization process. The final step is organizing those authorizations according to the roles and areas employees actually need to access.
How Can Canadian Organizations Structure Access Permissions by Employee Role?
Canadian organizations can structure physical access permissions by assigning employees only the building areas required for their responsibilities. This role-based approach separates public spaces, staff areas and restricted rooms, reducing unnecessary access without preventing employees from performing their work. It also provides a consistent framework for managing PINs, contractors and changes in employment responsibilities.
The first step is to identify the different security zones within the premises. A small commercial business may have several distinct access categories:
- Public areas: Reception, customer waiting spaces and other areas open to visitors during operating hours.
- Staff areas: Offices, employee facilities and internal operational spaces.
- Restricted areas: Back offices, stockrooms and maintenance spaces requiring additional authorization.
- Sensitive areas: Server rooms, cash storage areas and other locations containing valuable assets or sensitive information.
Once the zones are defined, the business can map employee roles to the areas required for their duties. For example, a receptionist may need access to reception and designated staff areas, while a maintenance contractor may only require access to specific technical spaces during an approved work period.
This follows the principle of least privilege: access should be limited to what a person needs rather than automatically extending to every area within the building.
The Canadian Centre for Cyber Security recognizes role-based physical access authorization in its guidance. Its framework supports maintaining approved access lists, reviewing permissions and removing individuals when access is no longer necessary.
Modern multi-user keypad controllers may support individual PINs, access schedules and different permission profiles. These capabilities can allow a business to restrict a credential to designated entrances or specific time windows, where the installed system provides those functions.
However, not every commercial keypad supports zone-based or time-restricted permissions. Businesses should verify the controller’s actual capabilities before assuming that role-based access can be implemented without additional equipment.
An access register provides the administrative foundation for this model. It should connect each credential to its holder, assigned areas and authorization status.
A useful register can contain:
- Employee or contractor name.
- Job title or operational role.
- Assigned PIN, badge or other credential identifier, without unnecessarily exposing the actual secret code.
- Authorized entrances and restricted zones.
- Permitted access periods, where supported.
- Credential issue, review and revocation dates.
- Person responsible for approving and maintaining the authorization.
Permissions should be reviewed when an employee joins, leaves or changes responsibilities. Promotions, transfers and lateral moves can make previously appropriate access rights unnecessary, even when the employee remains with the organization.
A twice-yearly review can serve as an internal governance choice for businesses seeking a recurring permission assessment. The appropriate frequency should reflect staff turnover, site sensitivity and operational risk rather than being presented as a universal Canadian requirement.
For smaller organizations, a straightforward access register and a clearly assigned administrator may be sufficient to establish consistent control. The important distinction is between having credentials programmed into a keypad and knowing why each credential remains authorized.
Five Actions to Strengthen Commercial Keypad Security
- Inventory every access point: Produce a list of entrances, keypads, locking hardware and associated access controllers.
- Identify credential holders: Create an access register showing every authorized employee, contractor and third party, including credential issue dates.
- Review PIN exposure: Identify shared, inherited, compromised or unnecessarily distributed codes and record the corrective action required for each.
- Establish a revocation process: Document who is responsible for removing credentials after employee departures, contractor expiry and changes in authorization.
- Map permissions to roles: Record which entrances and restricted areas each role requires, together with the date of the next permission review.
Role-based access management also makes the earlier security measures easier to maintain. Individual PINs can support accountability, controlled rotation can reduce credential exposure, and departure procedures can remove permissions without unnecessarily disrupting the rest of the organization.
For Canadian businesses, strengthening numerical PIN security is ultimately an ongoing management responsibility rather than a one-time hardware purchase. Combining controlled credentials, appropriate door hardware, reliable revocation procedures and regular permission reviews makes building access easier to administer while reducing opportunities for unauthorized entry. Businesses should begin by auditing existing credentials and correcting the most significant access-control weaknesses.
How often should a Canadian business change its commercial door PIN?
There is no universal PIN rotation frequency established by the Canadian government guidance discussed in this article. Businesses should assess credential exposure, staff turnover, the number of people sharing a code and the consequences of unauthorized access. A suspected compromise, lost device containing a PIN or employee departure involving a shared credential should trigger an immediate review rather than waiting for a scheduled change.
Are individual keypad PINs more secure than shared access codes?
Individual PINs generally offer better accountability because each credential can be associated with a specific authorized user. They also make it easier to revoke one person’s access without changing everybody else’s code. Shared codes may be operationally acceptable for small, low-risk teams, but they provide limited information about who entered the building. The RCMP recommends individual PINs for staff as a physical access security best practice.
Should contractors and cleaning staff receive the same door PIN as employees?
Contractors and cleaning personnel should receive only the access necessary to perform their work. Where the access-control system supports it, separate credentials with restricted schedules or designated zones can help prevent third-party access from becoming mixed with permanent employee credentials. Organizations should also document who receives these credentials and when their authorization ends.
Can a magnetic lock be installed on a commercial emergency exit in Canada?
Magnetic locks can be permitted in certain exit-door configurations, but their installation and operation must satisfy the applicable building and fire requirements. The National Building Code of Canada 2020 includes specific conditions for certain electromagnetic locking arrangements, including fire-alarm and power-loss release provisions. Because provinces and territories adopt and amend building codes, businesses should have the proposed installation reviewed by a qualified professional and the relevant local authority.
What information should a commercial door access register contain?
An access register should identify each credential holder, their role, the credential type, authorized entrances or zones, issue date, current authorization status and revocation date when applicable. It should also identify the person responsible for managing permissions. Avoid storing actual secret PINs in an unnecessarily accessible register. Regularly compare the register against the credentials programmed into the access-control system so that outdated or unidentified permissions can be investigated.