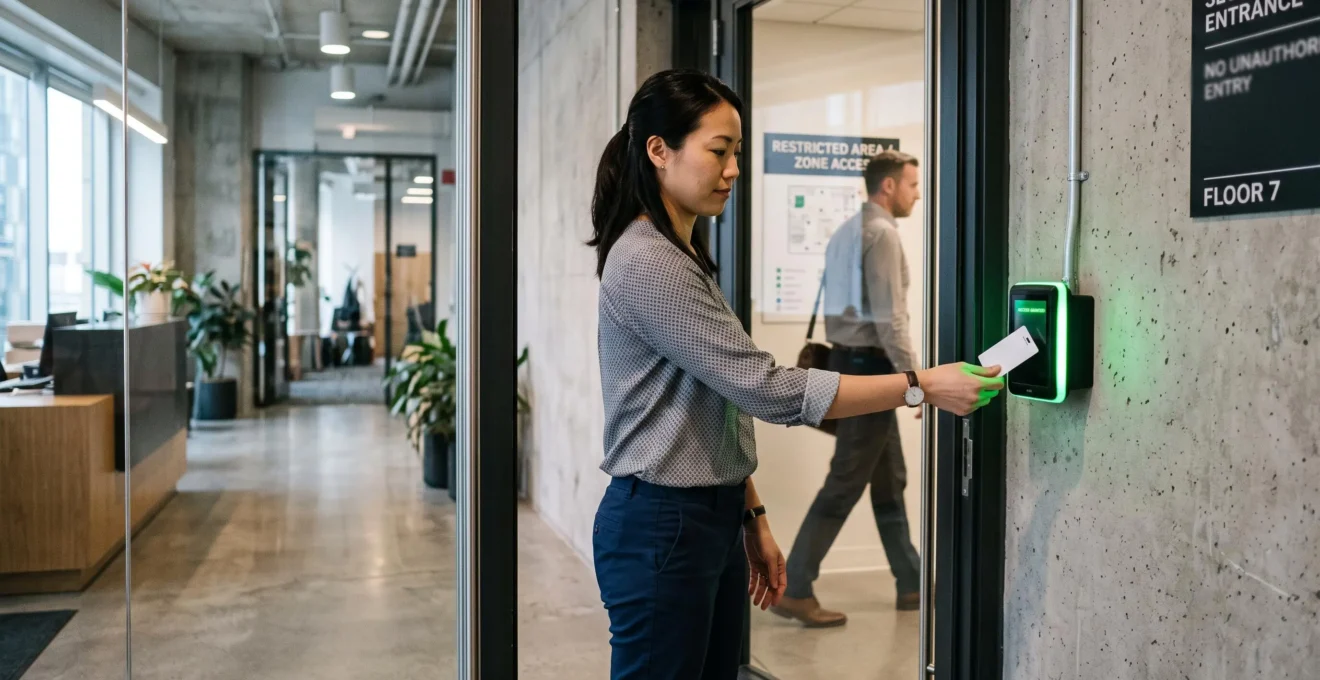
Businesses can secure restricted workplaces without slowing authorized employees by separating facilities into clearly defined access zones and matching each zone to specific permissions. The most effective approach combines visible physical boundaries, reliable electronic access controls, documented authorization rules and procedures for exceptional situations. Staff should understand where they can go, while the access system should recognize their permissions without requiring unnecessary approvals at every door.
For Canadian organizations protecting laboratories, archives and sensitive operational rooms, the challenge is to balance two requirements: preventing inappropriate access and preserving legitimate operational movement. A single undifferentiated restricted perimeter can create delays, while poorly defined boundaries can leave sensitive assets exposed. A layered zoning model provides a practical alternative, provided that its design reflects the sensitivity of the information or equipment, the building’s occupancy and the applicable regulatory requirements.
The objective is not to make every door difficult to open. It is to make authorization predictable, proportionate and verifiable, including during maintenance, emergencies and changes in staffing.
Restricted-zone security: the essentials
- Define distinct access zones with visible boundaries, documented floor plans and clear authorization criteria.
- Combine physical barriers with electronic permissions according to the sensitivity of each space and the frequency of legitimate access.
- Coordinate access permissions with staff roles, contractors, maintenance procedures and emergency-egress requirements.
- Why Unclear Restricted-Area Boundaries Lead to Access Violations
- How to Define Restricted Areas in a Shared Commercial Building
- Physical Barriers or Electronic Permissions for Research Laboratories
- Why Emergency Exit Arrangements Can Create Restricted-Zone Security Gaps
- When Should Businesses Establish Temporary Restricted Zones During Maintenance?
- Why Incorrect Lock Fail Modes Can Create Emergency Exit Hazards
- How Can Dual Authorization Protect Sensitive Equipment Rooms?
- How Can Canadian Organizations Structure Access Permissions by Employee Role?
Why Unclear Restricted-Area Boundaries Lead to Access Violations
Unclear restricted-area boundaries lead to access violations because employees cannot reliably distinguish permitted circulation from controlled space. When a doorway, corridor, stairwell or adjoining service room has no obvious status, staff must interpret the rules individually. An employee may cross a boundary without intending to enter a restricted area, creating an access incident that reflects a design or communication failure rather than deliberate misconduct.
This distinction matters when reviewing security incidents. A malicious intrusion involves an individual knowingly attempting to bypass an authorization requirement. An ambiguity-related violation occurs when the physical environment does not communicate that a restriction applies. Treating both situations as disciplinary failures can conceal the underlying weakness: the organization has not made its access boundaries sufficiently understandable.
Common sources of confusion include:
- Unmarked transitions: a public corridor leads directly into an operational or restricted room without a visible change in access status.
- Unclear adjoining spaces: employees cannot tell whether a stairwell, storage room or service passage belongs to the restricted perimeter.
- Inconsistent signage: different doors use different labels or identification systems for equivalent restrictions.
- Outdated floor plans: physical changes to the premises are not reflected in access documentation.
- Unclear authorization rules: staff know that a room is restricted but do not know which roles, approvals or escort arrangements permit entry.
A practical clarity audit should test what employees actually understand, not simply whether a security policy exists. Facilities managers can walk through each access point with employees from different departments and ask three questions: Is the space beyond this point restricted? Which roles may enter? What authorization or escort is required? The audit should include less obvious transitions, such as service corridors, shared stairwells and doors that connect operational areas.
Record each response against the relevant location. If employees give different answers about the same doorway, the boundary needs clarification. The corrective action may involve consistent signs, updated floor plans, physical demarcation, revised access permissions or targeted staff training. The objective is to make the restriction understandable before an employee reaches the controlled door.
Public Services and Procurement Canada‘s federal work-site security guidance provides a useful reference for this approach. It describes progressively restricted zones, controlled transitions and documented floor plans identifying perimeter entrances, internal access-control points and sensitive areas. Its model is relevant as a planning reference, although its complete hierarchy is not a universal legal requirement for every Canadian private-sector building. See Public Services and Procurement Canada’s work-site security requirements.
Ambiguous boundaries can also produce excessive restrictions. When security teams cannot determine exactly where a sensitive perimeter begins, they may impose broad access limitations to compensate for uncertainty. Authorized employees then face unnecessary detours, repeated badge checks or additional approvals. Clear boundaries therefore support both security and operational efficiency.
Once each boundary is understandable, the next challenge is deciding how those boundaries should work across a building occupied by several organizations with different responsibilities.
How to Define Restricted Areas in a Shared Commercial Building
Businesses in shared commercial buildings should define restricted areas through a documented zoning model that distinguishes public circulation, controlled transitions, tenant operations and sensitive spaces. Each zone needs an identifiable boundary, an accountable party and an authorization rule. This approach prevents one tenant’s security requirements from being confused with the building-wide access arrangements managed by the landlord or property operator.
A practical starting point is a four-level segmentation model:
- Public areas: entrances, reception spaces and other locations intended for general visitor access.
- Semi-restricted areas: controlled transition spaces where visitors may need identification, registration or an escort.
- Restricted areas: tenant operational spaces accessible only to authorized employees and approved visitors.
- Critical areas: particularly sensitive rooms or assets requiring stronger authorization and additional safeguards.
This four-level structure is a planning framework, not a prescribed universal Canadian legal classification. Public Services and Procurement Canada uses a five-zone model for its federal Contract Security Program context, distinguishing public access, reception, operations, security and high-security zones. Organizations can use that guidance to inform their own design while selecting categories appropriate to their premises and obligations.
The most difficult boundaries often involve shared infrastructure. Elevator lobbies, electrical rooms, telecommunications spaces, rooftops and shared server facilities may serve several tenants. No individual tenant should assume that its internal security policy automatically gives it authority to restrict a common area. The applicable lease, building-management agreement and operational responsibilities determine who can establish and enforce restrictions.
Before installing access controls, the landlord and tenants should establish:
- Who owns or manages the physical space.
- Who is responsible for approving access requests.
- Whether contractors require tenant authorization, property-management approval or both.
- How emergency access and maintenance responsibilities are coordinated.
- Which organization maintains the authoritative floor plans and access records.
Zone size also requires a deliberate trade-off. A large restricted perimeter is easier to administer because it involves fewer access points, but it may unnecessarily limit legitimate circulation. Smaller zones provide greater precision but increase the number of controlled doors, permissions and administrative tasks. The right configuration depends on the sensitivity of the protected asset, the frequency of movement and the number of employee roles requiring access.
A useful decision matrix considers three factors together: the consequences of unauthorized entry, the expected volume of legitimate traffic and the complexity of the authorization population. A highly sensitive archive with occasional access may justify a narrow, tightly controlled perimeter. A frequently used operational room may need a more accessible boundary supported by individual permissions and entry records.
Every agreed boundary should appear on a current floor plan, with entrances, internal access points and restricted assets clearly identified. The plan should be recognized by the relevant tenants and building operator, with responsibility for updates assigned explicitly. Without that shared reference, a restriction can be enforced inconsistently or conflict with legitimate building circulation.
After the building-wide boundaries are agreed, organizations managing laboratories must decide which combination of physical separation and electronic permissions provides appropriate control inside the facility.
Physical Barriers or Electronic Permissions for Research Laboratories
Research laboratories generally benefit from combining physical barriers with electronic access permissions rather than relying exclusively on either approach. Physical separation establishes the laboratory’s security perimeter, while electronic controls distinguish authorized personnel within that perimeter. This layered arrangement can protect sensitive equipment and regulated materials without imposing the same access restrictions on every researcher working in the facility.
The two approaches solve different problems. A locked laboratory entrance prevents general circulation into the workspace, but it cannot distinguish a researcher who is authorized to use a particular instrument from a colleague who is not. Electronic permissions can make that distinction through individual credentials and role-specific authorization.
The main differences are operational:
| Criterion | Physical barriers | Electronic permissions |
|---|---|---|
| Granularity | Control access to a room, corridor or defined physical area. | Can distinguish individual users and authorization levels within the same facility. |
| Traceability | May provide limited individual entry information unless combined with monitoring or access records. | Can associate access attempts with individual credentials and recorded events. |
| Revocation | May require changing locks, recovering keys or updating physical key-control arrangements. | Permissions can be withdrawn through the access-management system, subject to its operation. |
| Failure exposure | Depends on the mechanical condition and configuration of the barrier. | Depends on power, controllers, credentials, databases and backup arrangements. |
| Best application | Establishing a clear physical perimeter around a laboratory or containment area. | Managing different authorization levels for equipment rooms and sensitive internal spaces. |
A layered configuration could use a controlled physical entrance for the laboratory, electronic permissions for equipment rooms and additional controls for sensitive storage. A postdoctoral researcher, laboratory technician and principal investigator could therefore have different permissions within the same general facility. The exact permissions should reflect their assigned duties rather than their job titles alone.
Canadian laboratories handling regulated human or terrestrial animal pathogens and toxins must also consider the applicable biosafety requirements. The Public Health Agency of Canada’s Canadian Biosafety Standard, Third Edition, addresses containment-zone boundaries, warning signage, lockable separation, access-control systems and personnel authorization. Its requirements depend on containment level, materials and activities; they should not automatically be applied to ordinary laboratories that do not handle regulated biological materials.
The standard also addresses backup mechanisms for electronic access control in specified containment environments, as well as the supervision or training of temporary visitors, maintenance personnel and contractors. Its third edition and Biosecurity Addendum continue to apply following the March 26, 2026 amendments to the Human Pathogens and Toxins Act, pending further updates. Organizations should check the applicable requirements for their specific facility rather than assume that one configuration satisfies every regulatory obligation. The relevant reference is the Public Health Agency of Canada’s Canadian Biosafety Standard.
Electronic permissions introduce a separate operational dependency. A power failure, controller malfunction, database error or damaged credential can prevent an otherwise authorized employee from entering. Laboratories should therefore establish documented backup arrangements appropriate to their containment and security requirements. Those arrangements must preserve safe emergency egress and avoid turning a technical failure into an uncontrolled shutdown or indiscriminate release of access.
The most effective design assigns a clear function to each layer: physical barriers define the perimeter, electronic permissions manage individual authorization, and documented contingency procedures preserve safe operations when technology is unavailable.
Even a well-designed laboratory perimeter can be undermined by doors that must serve two different purposes: preventing unauthorized entry and allowing occupants to evacuate safely.
Why Emergency Exit Arrangements Can Create Restricted-Zone Security Gaps
Emergency exits can create restricted-zone security gaps because doors designed for safe evacuation must remain usable from the inside, while security teams also need to prevent unauthorized entry from outside. The solution is to distinguish exit permission from entry permission. A properly designed arrangement can allow occupants to leave without a key or special authorization while maintaining appropriate controls against entry through the same door.
This distinction changes how a restricted perimeter should be mapped. An emergency exit is not necessarily a conventional security entrance. Its function may be to provide an escape route rather than a routine access point. Treating it as an ordinary locked door can create a serious conflict between physical security and occupant safety.
Access-control arrangements should therefore be evaluated according to the door’s actual function, the applicable occupancy classification and the locally adopted building and fire requirements. The National Building Code of Canada 2025 provides a national model framework for building safety and means of egress, but it does not automatically become enforceable legislation in every province or territory. Provincial and territorial authorities determine which provisions apply and may adopt different editions or modifications.
Several technical arrangements can help reconcile controlled entry with emergency evacuation:
- Controlled entry with independent egress: an electronic reader controls entry, while compliant exit hardware permits occupants to leave from the inside.
- Fire-alarm integration: where required by the applicable design and code provisions, the door-control system responds to the fire-alarm condition.
- Monitored emergency doors: door-position monitoring can identify unauthorized opening or prolonged door-open conditions.
- Approved release hardware: panic hardware and other permitted release mechanisms allow occupants to operate the exit without special knowledge.
These arrangements must be selected and installed by qualified professionals familiar with the applicable local requirements. Not every electronic lock requires the same fire-alarm response, and not every door can be configured using the same release mechanism. An improvised modification that prevents safe evacuation is dangerous and may violate applicable building or fire requirements.
Security gaps can also emerge from how people use emergency doors during ordinary operations. Employees may begin using an emergency exit as a convenient entrance to avoid a controlled lobby or badge reader. A door that connects a public corridor to a sensitive operational space may also create an unintended route into the restricted perimeter. These behaviours can weaken access control even when the original installation is technically compliant.
Another concern arises when evacuation routes cross sensitive rooms or expose the location of protected assets. The priority must remain safe evacuation, but security planners should understand which areas become accessible during an emergency and what information may be exposed through the route. Any additional controls must remain compatible with the applicable egress requirements.
The National Building Code of Canada 2025 is a model code, not a universal substitute for provincial or territorial requirements. Its provisions address exit-door operation and occupant safety, but the applicable rules depend on the building’s jurisdiction, occupancy and door configuration. The relevant model-code reference is the National Building Code of Canada 2025.
A structured exit review should classify each door as an exit-only route, a controlled-entry point with independent egress, or an evacuation route that passes through a sensitive area. Facilities managers should then compare the actual installation with approved drawings, the applicable local code and relevant insurance requirements.
Once emergency doors and their functions are understood, organizations can apply the same discipline to temporary access changes during maintenance and construction work.
When Should Businesses Establish Temporary Restricted Zones During Maintenance?
Businesses should establish temporary restricted zones whenever maintenance work changes the normal security boundary, exposes sensitive infrastructure or introduces external personnel into areas they would not ordinarily access. Temporary controls are particularly important when contractors work near server rooms, electrical systems, telecommunications cabling, service ducts or normally sealed partitions. The restriction should last only as long as the additional exposure requires.
Maintenance creates a distinctive security challenge because routine building operations often require temporary exceptions. Contractors may need to remove access panels, open walls, disconnect equipment or work in areas where sensitive assets are normally protected. Without a defined temporary perimeter, the work can create additional access routes that are not covered by the permanent security plan.
Common triggers include:
- Work involving exposed network cabling, telecommunications infrastructure or server-room connections.
- Repairs requiring access to electrical, mechanical or other sensitive service rooms.
- External contractors entering restricted areas without an established authorization history.
- Temporary removal of doors, partitions, locks or other physical security barriers.
- Emergency repairs that require immediate access to infrastructure normally kept restricted.
A temporary zone should have a defined perimeter, a responsible supervisor and an expected end time. External personnel should receive access limited to the locations and duration required for the work. Where the access-control system supports it, temporary credentials should expire automatically rather than remain active indefinitely.
Regular employees should also receive practical information about the temporary arrangement. They need to know which routes are affected, whether normal access permissions have changed and who can authorize exceptions. This reduces accidental entry and discourages informal workarounds.
Maintenance work should not create permanent access rights by accident. A contractor may receive a temporary badge, a temporary key or a supervised exception to complete a specific task. When the work ends, the organization should explicitly close the temporary arrangement rather than assume that the original permissions will disappear automatically.
A documented closeout should verify:
- Temporary badges, keys and other credentials have been returned or deactivated.
- Contractor access permissions have expired or been revoked.
- Removed barriers, doors and access-control devices have been restored.
- Temporary changes to the floor plan or access routes have been reviewed.
- Outstanding security issues have been assigned to a responsible person.
Urgent repairs require a controlled exception rather than an abandonment of access rules. Organizations should establish in advance who can approve emergency entry, what identity verification is required and what level of supervision is practical. The resulting access should be recorded and reviewed after the incident, especially when normal authorization procedures could not be followed.
Public Services and Procurement Canada’s federal work-site security guidance recognizes that contractors, maintenance workers and cleaning personnel entering security zones must meet applicable clearance or escort requirements. Its specific provisions apply within the relevant federal contract-security context, but the underlying need to control and supervise temporary access is also useful when designing private-sector procedures.
The following checklist translates these principles into a verifiable maintenance-control process.
Five actions to control temporary maintenance access
- Define the temporary perimeter: produce a marked floor-plan extract showing affected rooms, entrances, alternative routes and the work area.
- Assign access responsibility: record the approving manager, contractor identities, permitted locations and applicable supervision arrangements.
- Set the access duration: document the start and expected end time, together with the temporary badge or key-control arrangements.
- Communicate the restriction: distribute a maintenance notice identifying affected routes, temporary boundaries and the person responsible for exceptions.
- Complete the closeout: retain a signed record confirming credential revocation, barrier restoration and resolution or assignment of outstanding security issues.
These five deliverables create an auditable record of the temporary security arrangement. They also make it easier to identify access that has remained active after the operational reason for granting it has disappeared.
Temporary access management is only one part of the problem: the underlying lock configuration must also behave correctly when power is interrupted or an emergency occurs.
Why Incorrect Lock Fail Modes Can Create Emergency Exit Hazards
Incorrect lock fail modes create emergency exit hazards when a door’s behaviour during power loss conflicts with its intended function. A fail-safe lock generally releases when its power supply is interrupted, while a fail-secure lock generally remains locked. Neither configuration is automatically appropriate for every door. The correct arrangement depends on whether the door controls entry, provides emergency egress or performs both functions through separate mechanisms.
The distinction is particularly important in restricted facilities. Security teams may assume that a sensitive room should remain locked under every circumstance. However, a lock that prevents safe evacuation can create a life-safety hazard. Conversely, configuring every entrance to release automatically during a power failure can expose sensitive areas to unauthorized entry.
| Configuration | Typical behaviour | Security and safety consideration |
|---|---|---|
| Fail-safe | The electrically controlled locking mechanism releases when power is lost. | May preserve access or egress depending on the door arrangement, but can expose a restricted entrance. |
| Fail-secure | The electrically controlled locking mechanism remains locked when power is lost. | May preserve perimeter security, but must not prevent required emergency egress. |
| Independent mechanical egress | Occupants can operate an approved mechanical release independently of the electronic entry-control system. | Can allow controlled entry and safe exit when designed and approved for the particular door. |
The important distinction is between the lock’s electrical state and the door’s complete egress function. A fail-secure electronic entrance does not necessarily mean that occupants are trapped inside. A compliant mechanical release may permit immediate exit even while the electronic locking mechanism remains secure against entry from the other side.
Likewise, a fail-safe configuration is not automatically the best choice for a sensitive entrance. If an interruption releases the locking mechanism, unauthorized individuals may be able to enter the restricted area. The organization must evaluate the consequences of that behaviour alongside evacuation requirements and any approved emergency release arrangements.
Canadian building requirements must be checked at the provincial or territorial level. The National Building Code of Canada is a model code, and local authorities determine which edition and modifications apply. Door hardware requirements can also vary according to occupancy classification, door function and the type of electronic locking arrangement. A generic statement that every emergency door must unlock in exactly the same way during every alarm condition is therefore unreliable.
Security managers should avoid specifying fail-safe or fail-secure equipment solely from a room’s sensitivity classification. Instead, they should document the function of each door, identify the permitted entry and exit arrangements, and obtain confirmation from qualified access-control and life-safety professionals.
Commissioning should include practical testing under controlled conditions. For each relevant door, verify the normal operating state, the response to a power interruption, the operation of any backup supply and the mechanical exit function. Where appropriate, the test should also cover fire-alarm integration and restoration after the emergency condition ends. A depleted backup battery should not be overlooked when assessing the actual failure behaviour.
Testing must be planned with the responsible building and fire-safety personnel so that it does not create an uncontrolled security or evacuation risk. Results should be recorded against the individual door, including its hardware configuration and any corrective actions.
Once individual door behaviour has been validated, organizations can consider whether particularly sensitive rooms require more than one person’s authorization for entry.
How Can Dual Authorization Protect Sensitive Equipment Rooms?
Dual authorization protects sensitive equipment rooms by requiring two independent approvals before access is granted or a critical operation can proceed. Depending on the system, this may involve two authorized individuals physically present or one employee supported by a separate remote approval. The objective is to reduce reliance on a single person’s judgement and create an additional accountability point for sensitive activities.
This approach is commonly described as the two-person rule or dual authorization. It is most useful when unauthorized access could have significant operational, financial, safety or information-security consequences. A sensitive telecommunications room, a critical server environment or a facility containing infrastructure that supports physical security may justify stronger authorization than an ordinary storage room.
However, requiring two people for every restricted door can create unnecessary operational friction. The control should be proportionate to the impact of compromise and the frequency of legitimate access.
A decision should consider:
- Consequence of compromise: could one person’s unauthorized action interrupt a critical service, expose sensitive information or disable an important security function?
- Access frequency: how often must authorized staff enter to maintain normal operations?
- Availability of authorized personnel: can the organization reliably provide two eligible people during normal hours and emergencies?
- Independence of approval: does the second authorization provide a genuinely separate check rather than simply repeating the first person’s decision?
- Operational alternatives: could individual permissions, entry logging or supervised access provide sufficient protection with less disruption?
Two-person access should not become a routine ritual in which the same colleagues automatically approve each other’s requests. Such a pattern can reduce the independence of the control and encourage informal workarounds.
Organizations can strengthen the process through several operational arrangements:
- Rotate authorized pairs to avoid relying consistently on the same individuals.
- Record both approvals and the identities of the people involved.
- Use an access-control system that associates both authorizations with the relevant entry event where supported.
- Allow a designated supervisor to approve exceptional access outside normal operating hours.
- Review unusual access events and repeated exceptions to identify weaknesses in the procedure.
The distinction between two people physically present and two independent approvals is important. A remote approval can provide a second authorization point, but it does not necessarily provide the same physical observation or immediate intervention as a second person inside the room. Organizations should select the method according to the risk being controlled.
Emergency access presents another challenge. A critical equipment failure may require immediate intervention when a second authorized person is unavailable. A strict rule with no exception mechanism could prolong an outage or delay essential repairs.
A better approach is to establish an auditable emergency exception. The procedure should identify who can authorize it, what justification must be recorded, how the access event is logged and who reviews the exception afterwards. The emergency process should be sufficiently clear to prevent an informal bypass from becoming the normal operating method.
Dual authorization is a risk-based security control, not a universal Canadian regulatory requirement for every sensitive equipment room. The Canadian Biosafety Standard, for example, contains specific access-control and authorization provisions for regulated containment environments, but it does not establish a general two-person authorization rule for all laboratory or equipment rooms.
Dual authorization adds a second layer of accountability, but it works best when embedded in a broader permissions structure that keeps everyday access aligned with each employee’s actual responsibilities.
Key decisions before implementing role-based access
- Assign permissions according to documented responsibilities rather than seniority or convenience alone.
- Coordinate physical access changes with employee onboarding, internal transfers and departures.
- Review existing permissions against current roles and the sensitivity of the information or facilities protected.
How Can Canadian Organizations Structure Access Permissions by Employee Role?
Canadian organizations can structure physical access permissions by employee role through role-based access control (RBAC). Instead of assigning every badge individually to every door, the organization defines operational roles and connects each role to the zones its members need to enter. This makes permissions easier to administer, review and adjust when employees join, change responsibilities or leave the organization.
A practical role-based model might distinguish the following groups:
| Employee or user role | Typical access scope | Authorization considerations |
|---|---|---|
| General employee | Public, reception and designated operational areas. | Access follows normal workplace responsibilities. |
| Restricted-zone personnel | Specific controlled rooms and operational zones. | Permissions depend on assigned duties and required training. |
| Technical personnel | Approved service rooms, infrastructure areas and maintenance locations. | Access may be restricted by work order, location or time period. |
| Senior management | Designated management and operational areas. | Seniority alone should not automatically confer access to every sensitive asset. |
| External contractors | Only the locations required for an approved assignment. | Temporary authorization, identity verification and escort arrangements may apply. |
These categories are illustrative rather than mandatory. A laboratory, financial institution, public utility and commercial archive may require very different role definitions. The appropriate model should reflect the organization’s operating structure and the sensitivity of its protected spaces.
The central principle is need-to-know and need-to-access. Employees should receive the physical permissions necessary to perform their duties, not unrestricted access simply because they belong to the organization. An employee working in a general administrative department may need access to an ordinary office but have no operational reason to enter a server room or a controlled archive.
Role-based permissions also improve the consistency of personnel changes. Human resources and security administration should coordinate the physical access implications of onboarding, internal transfers and departures. A change of department may require a new permission set, while a departure should trigger the organization’s documented credential-revocation process.
Physical access should be considered alongside information-system permissions, but the two systems do not necessarily share the same technical architecture or administrative workflow. A change to a person’s IT account should not be assumed to update their physical badge automatically. Organizations should define the responsible teams, the notification process and the confirmation required to establish that the change has been completed.
For organizations subject to Canada’s Personal Information Protection and Electronic Documents Act (PIPEDA), the Office of the Privacy Commissioner of Canada recommends safeguards proportionate to the sensitivity of personal information. Its guidance includes physical restrictions, organizational measures, employee training, need-to-know access and regular reviews of security arrangements.
PIPEDA does not prescribe one particular access-control technology or mandate role-based access control as a specific implementation. Nor does it establish a universal same-day physical-badge revocation deadline or a fixed annual access-review interval. Applicability must be assessed in light of the organization’s activities and the relevant federal or provincial privacy framework. The regulator’s explanation is available in the Office of the Privacy Commissioner’s guidance on PIPEDA safeguards.
Access reviews should compare the current list of badge holders and permissions against the organization’s latest staff and role records. The purpose is to identify discrepancies that could otherwise remain unnoticed, including:
- Employees retaining access to rooms no longer required for their responsibilities.
- Former employees whose credentials remain active.
- Staff who have transferred departments without corresponding permission changes.
- Contractors retaining permissions after their assignments have ended.
- Roles that grant broader access than the actual operational requirements justify.
Review frequency should reflect the sensitivity of the protected areas, the rate of organizational change and the applicable regulatory obligations. Particularly sensitive environments may warrant more frequent checks or additional reviews after significant personnel changes.
Access records should also support accountability. When an incident occurs, security teams should be able to establish which credentials were authorized, which access attempts were recorded and whether the permissions were appropriate at the time. This makes the access model a practical operational control rather than simply an administrative classification exercise.
For Canadian organizations operating in regulated sectors such as healthcare, finance and public services, role-based access can also support the demonstration of appropriate safeguards. However, privacy and security obligations vary according to the sector, the information involved and the applicable federal or provincial legislation.
The next practical step is to compare existing badge permissions with current job responsibilities and documented zone boundaries. Organizations that identify unnecessary access, clarify ownership and establish reliable review procedures can strengthen restricted-area protection while keeping legitimate staff movement predictable and efficient.
What is the most effective way to secure a restricted area without delaying employees?
The most effective approach combines clearly marked physical boundaries with role-based electronic access permissions. Employees should receive access to the specific areas required for their responsibilities, while more sensitive rooms receive additional controls where justified. This avoids applying unnecessarily restrictive rules to the entire facility.
How many security zones should a Canadian business establish?
There is no universal number for every Canadian business. A four-level model covering public, semi-restricted, restricted and critical areas can provide a useful starting point. Public Services and Procurement Canada describes a five-zone model for federal contract-security environments. The appropriate structure depends on the organization’s assets, operations and applicable obligations.
Should electronic access control replace physical security barriers?
No. Electronic access control and physical barriers serve complementary purposes. Physical barriers establish the protected perimeter, while electronic permissions distinguish individual authorization levels. Combining them can provide more precise control, particularly in laboratories, server rooms and sensitive operational facilities. Backup arrangements must also address technical failures.
Can an emergency exit remain locked from the outside in a restricted facility?
Controlled entry may be compatible with emergency egress, provided the door and its release hardware meet the applicable building and fire requirements. The specific configuration depends on the door’s function, building occupancy and provincial or territorial code provisions. A qualified professional should verify the installation rather than relying on a generic lock configuration.
How often should organizations review employee access permissions?
Review frequency should reflect the sensitivity of the protected areas, staff turnover, internal transfers and applicable regulatory requirements. Reviews should also follow significant personnel changes and identify former employees, outdated contractor credentials and permissions that no longer match operational responsibilities. Canadian privacy guidance supports regular safeguard reviews but does not establish one universal review interval.