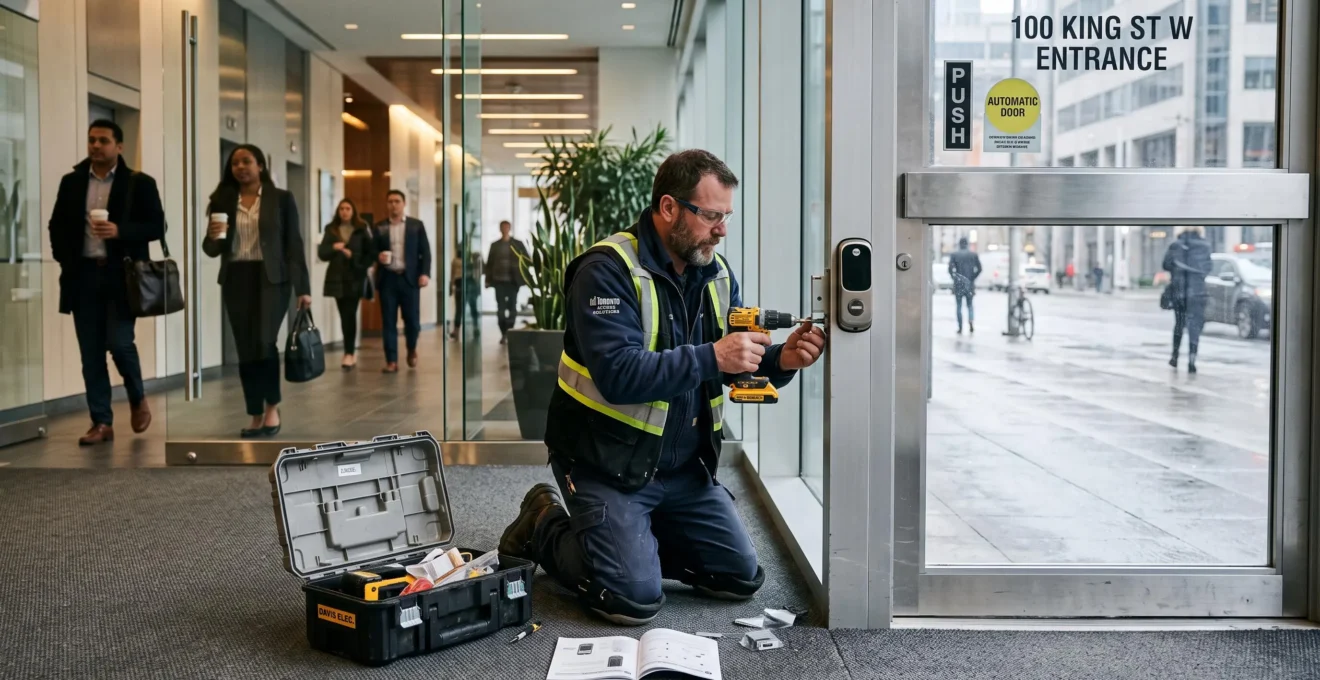
Canadian businesses can replace mechanical keys with electronic access control systems without shutting down their offices by auditing existing doors, selecting compatible hardware and deploying credentials in controlled phases. The critical requirement is maintaining reliable building access and legally compliant emergency exits throughout installation.
A successful retrofit begins with the building rather than the software. Door construction, existing locks, available wiring, fire-safety requirements and employee movement patterns determine which access technologies are appropriate. A wireless lock may suit one internal office door, while a networked controller and electric strike may be better suited to a frequently used main entrance.
Operational planning is equally important. Employees need working credentials before a door changes over, maintenance contractors need predictable access, and facilities teams must be able to revoke permissions when staff leave. Canadian building and fire regulations also vary by jurisdiction, making local compliance verification essential before equipment is ordered.
The following approach connects hardware selection, installation scheduling, credential management and long-term system maintenance into a practical deployment strategy.
Electronic access control implementation: Key decisions
- Audit and classify doors before installation, then retrofit them in phases while preserving existing entry arrangements during verified transition periods.
- Choose standalone, networked or hybrid access control according to credential turnover, security sensitivity and administrative requirements rather than office size alone.
- Verify emergency egress, establish timely credential revocation and manage access logs under applicable Canadian privacy requirements.
- Why Do Lost Mechanical Keys Create Long-Term Security Problems for Offices?
- How Can You Install Electronic Access Control in an Existing Office Building?
- Standalone Smart Locks or Networked Access Control for Small Offices?
- Why Incorrect Lock Fail Modes Can Create Emergency Exit Hazards
- When Should a Business Replace Its Existing Electronic Door Controls?
- Mobile Credentials or Physical Key Fobs for Hybrid Office Workers?
- How Can Facilities Track Contractors Without Delaying Maintenance Work?
- How Can Canadian Organizations Manage Digital Access Credentials as Staff Changes?
Why Do Lost Mechanical Keys Create Long-Term Security Problems for Offices?
Lost mechanical keys create persistent office security risks because individual keys generally cannot be deactivated without changing the corresponding lock or cylinder. Any unaccounted-for copy may continue operating indefinitely. Electronic credentials provide a more manageable alternative because authorized administrators can revoke individual permissions without replacing the door hardware, provided the system receives and applies the revocation.
The problem extends beyond the immediate possibility of unauthorized entry. Mechanical keys are physical duplicates of an authorization that the building cannot selectively withdraw. When a key disappears, facilities personnel must determine whether the associated cylinder should be rekeyed or replaced and whether other entrances use the same key.
That decision can trigger a chain of operational work:
- Identify every door operated by the missing key, including any master-key permissions.
- Arrange locksmith work and potentially restrict access while locks are changed.
- Issue replacement keys to employees, cleaners and authorized contractors.
- Update key registers and account for previously distributed copies.
- Coordinate replacement access arrangements to keep employees moving.
Because these activities require coordination and expenditure, some businesses postpone rekeying. Delaying the decision also prolongs uncertainty about who might possess a functioning key.
Not every lost-key incident warrants an identical response. A key whose location and custody remain reasonably established presents a different exposure from one lost alongside an employee badge identifying the building. A missing master key, a key discovered absent after an employee departure, or a key lost close to the premises calls for greater scrutiny.
A practical assessment should document the key’s permissions, the circumstances of loss, the likelihood of identification or misuse, and the consequences of unauthorized entry. The resulting response may range from a documented review to immediate rekeying.
The NIST-hosted security-control framework for electronic physical access systems identifies lost keys, compromised combinations and personnel changes as conditions requiring appropriate physical-access security measures. This US technical guidance offers useful security-management principles but does not establish Canadian commercial-building obligations.
Digital revocation changes the underlying security model. Instead of replacing a shared physical authorization, an administrator can disable one credential while leaving others active. The effective timing depends on whether readers and locks communicate with the management system immediately or synchronize periodically.
The next decision is how to introduce that technology without interrupting the building’s existing access arrangements.
How Can You Install Electronic Access Control in an Existing Office Building?
Installing electronic access control in an occupied office requires a door-by-door assessment followed by a phased retrofit. Facilities teams should identify suitable lock technologies, confirm emergency-exit requirements, enrol users before activation and schedule changes outside busy periods. Existing keys or other approved access arrangements should remain available until each replacement door has passed operational testing.
Start with an inventory of every proposed controlled opening. Record its function, door and frame material, existing hardware, electrical infrastructure, fire rating, expected traffic and whether it forms part of a required exit route.
Then classify doors by operational importance. Main entrances generally require the most careful transition planning because an access failure could affect the entire workforce. Restricted storage, server rooms and internal offices can often be scheduled separately.
Several retrofit approaches may reduce construction requirements:
- Wireless battery-powered electronic locks: Potentially suitable for compatible internal doors where running new control wiring would be difficult. Battery maintenance, network coverage and hardware certification still require evaluation.
- Electric strike retrofits: May preserve compatible mechanical door hardware while electronically controlling entry. Frame construction, latch geometry, fire rating and exit operation determine suitability.
- Secure-side door controllers: Positioning sensitive control components inside a protected area can reduce exposure to tampering, provided wiring and system architecture support the installation.
Metal frames require inspection for suitable wiring routes and hardware preparation. Glass storefront entrances may need specialized hardware compatible with existing door assemblies. Heritage buildings in Canadian downtown areas can introduce additional physical and approval constraints, making less invasive solutions desirable where permitted.
Fire and building-code checks must precede hardware purchasing. For example, Ontario Fire Code requirements for exit doors and locking devices regulate exit-door operation and establish conditions for certain electromagnetic locking arrangements. These rules apply in Ontario; installations elsewhere in Canada require evaluation under the relevant provincial or territorial requirements and approved building design.
A controlled transition can be organized around five deliverables rather than a single building-wide cutover.
Five checks before activating an electronic door
- Inspect the door, frame, existing hardware and exit function; produce a signed door-condition record.
- Select compatible locking and control equipment; prepare a door-specific hardware and compliance specification.
- Register authorized employees and contractors; generate a verified credential enrolment list.
- Schedule installation and maintain an approved temporary access method; publish the changeover schedule and fallback instructions.
- Test authorized entry, denied entry, power-loss behaviour and required emergency operation; retain a commissioning record before withdrawing the previous access method.
Credential issuance should begin before installation day. When safe and supported by the hardware, old and new access methods can operate in parallel during transition. Changes to main entrances should avoid morning arrival periods, and a responsible facilities contact should remain available to resolve access failures.
The building should not lose a functioning access route simply because one component is awaiting configuration. Each door group should be commissioned and accepted before the next group is changed.
Once the retrofit sequence is established, the choice between locally managed locks and centralized access control determines how much ongoing administration the building will require.
Standalone Smart Locks or Networked Access Control for Small Offices?
Standalone smart locks suit offices with relatively few credential changes and limited reporting requirements. Networked access control is generally more appropriate when administrators need centralized permissions, scheduled access or consistent audit records across multiple doors. A small office can also combine the two approaches, using centralized control for sensitive entrances and standalone locks elsewhere.
The distinction is primarily administrative. Standalone locks can operate independently and may store credentials locally, whereas networked systems coordinate permissions through connected controllers or management software. Actual features vary by product, so standalone does not automatically mean offline or incapable of remote management.
The following comparison identifies the capabilities that buyers should verify rather than assuming every device in a category behaves identically.
| Decision criterion | Standalone smart locks | Networked access control |
|---|---|---|
| Credential management | Typically managed per lock or through a vendor-specific application; capacity varies. | Typically supports centralized administration across connected doors. |
| Audit records | May offer local or application-based event history; detail and retrieval vary. | Usually supports aggregated events and broader reporting functions. |
| Revocation | May require local synchronization, physical programming or compatible remote connectivity. | Can distribute changes centrally, subject to controller connectivity and synchronization. |
| Ownership costs | Potentially simpler initial installation, with battery and per-door maintenance costs. | Additional infrastructure, software and support costs, potentially offset by centralized administration. |
| Failure behaviour | Depends on battery condition, lock design and local programming. | Depends on controllers, power supply, connectivity and configured local operation. |
The most revealing question is not how many people work in the office, but how frequently permissions change. A business with a handful of doors and frequent contractor rotations can have more demanding administration than a larger workplace with stable staffing.
For example, consider a hypothetical three-door office with a main entrance, server room and general storage room. The business could choose networked control for the entrance and server room while retaining a compatible standalone lock for storage. This avoids centralizing a low-sensitivity opening unnecessarily while keeping critical permissions easier to manage.
However, a hybrid deployment must still be managed as a coherent security program. Facilities personnel need an inventory of credentials, responsibility for each platform and a clear procedure for removing access when somebody leaves.
Indicators that centralized management may be worthwhile include recurring monthly permission changes, cleaner and contractor schedules, remote revocation requirements and a need to investigate entry events across multiple doors.
Audit requirements deserve particular scrutiny. A lock reporting that a credential was accepted records a system event, not conclusive proof that the assigned person entered alone. Tailgating and credential sharing can limit the evidentiary value of logs.
Whichever architecture is selected, its electrical and mechanical behaviour must be evaluated against the building’s emergency-exit requirements before installation.
Why Incorrect Lock Fail Modes Can Create Emergency Exit Hazards
Incorrect electronic lock fail modes can create emergency hazards when a power failure leaves occupants unable to use a required exit. Fail-safe locks release when electrical power is lost, while fail-secure locks remain locked in their electrically controlled direction. The correct configuration depends on the complete door assembly, applicable codes and whether occupants can exit through an independent compliant release mechanism.
Fail-safe and fail-secure describe what the electrically operated locking component does when power disappears. They do not, by themselves, establish whether the entire door provides lawful emergency egress.
A fail-secure electric strike may continue preventing entry from the corridor while an independent mechanical lever or panic device permits normal exit from inside. Conversely, an improperly configured electromagnetic lock can create a serious concern if its release depends on power, sensors or controls that do not operate as legally required.
The essential test is the actual exit-side operation, not the terminology printed on the lock specification.
For doors designed to permit ordinary mechanical egress, facilities personnel should verify that occupants can operate the prescribed exit hardware without presenting credentials, accessing a smartphone or relying on electrical power. Any code-permitted specialized or controlled-egress arrangement must instead be assessed against its approved requirements.
Commissioning should also evaluate the relationship between access control, fire-alarm interfaces and emergency power where applicable. A fire-alarm signal may be required to release certain electrically controlled locking arrangements, but the exact response depends on the approved design and local requirements.
In Ontario, Fire Code provisions address the operation of doors forming part of exits and access-to-exit routes. Specific provisions also govern electromagnetic locking devices and inspection obligations. These requirements cannot be generalized unchanged across every Canadian jurisdiction.
A door-by-door verification record should document:
- The locking component’s power-loss state and the resulting entry-side security behaviour.
- The approved method of releasing the door from the exit side.
- Any required fire-alarm or emergency-release interface.
- Observed operation during the specified power-loss and emergency tests.
- The responsible technician, test date and outstanding corrective actions.
Changes to a lock, controller, power supply or door closer may affect the approved arrangement. For that reason, records should remain linked to the individual opening throughout its service life.
Life-safety verification is also an important part of later modernization projects, because a controller replacement should never silently change how an existing exit operates.
When Should a Business Replace Its Existing Electronic Door Controls?
A business should consider replacing electronic door controls when the system can no longer provide dependable credential revocation, supported security maintenance, usable audit records or required integrations. Equipment age alone is an incomplete indicator. A controlled migration can preserve compatible readers, wiring and door hardware while replacing obsolete management components without a simultaneous building-wide cutover.
One warning sign is a discontinued credential technology. If replacement cards or fobs are increasingly difficult to procure, the building becomes dependent on a shrinking supply of compatible devices. Another is the loss of software security updates for controllers that remain connected to operational networks.
Facilities personnel should also investigate repeated technician visits for routine administrative changes, unreliable synchronization and log-export limitations that obstruct incident reviews.
A practical replacement assessment compares the existing system’s annual operational burden against a proposed migration:
- Record recurring software, support and credential charges.
- Summarize technician callouts and internal administration time.
- Identify unsupported components and their operational consequences.
- Obtain project-specific estimates for compatible replacement equipment and installation.
- Compare ongoing maintenance requirements and the disruption associated with each option.
This is a decision framework, not proof that modernization will always be cheaper. Savings depend on the actual equipment inventory, service agreements and compatibility constraints.
Interoperability should be checked before hardware is removed. The Security Industry Association‘s OSDP standard information describes a reader-to-controller communication protocol supporting bidirectional communication, supervision and secure-channel capabilities.
OSDP can help reduce dependence on certain proprietary reader interfaces, but it does not guarantee that existing readers will work with every new controller. Protocol versions, credentials, enabled functions and software configurations must all be checked. Existing wiring and power arrangements also require assessment.
The transition itself should follow door groups rather than a single cutover date. Administrators can prepare new credentials in batches, commission the replacement system on selected doors and verify users before retiring corresponding legacy components.
Where supported, parallel operation can protect continuity during migration. Where two locking systems cannot safely or practically operate together, temporary access arrangements should be established instead.
Legacy panels should be decommissioned only when their associated doors, users, emergency functions and logging requirements have been verified on the replacement platform.
Once a dependable platform is in place, choosing appropriate employee credentials becomes the next operational decision, particularly where office attendance varies throughout the week.
Mobile Credentials or Physical Key Fobs for Hybrid Office Workers?
Mobile credentials are often convenient for hybrid employees because compatible systems can issue and revoke access remotely without distributing physical devices. Key fobs remain useful when employees cannot rely on personal smartphones, work in phone-restricted areas or need predictable physical tokens. Supporting both credential types through one management platform provides flexibility without creating separate authorization policies.
Hybrid working introduces unusual access patterns. An employee may visit the office infrequently, start work remotely or change their usual location. Requiring an on-site appointment to collect a fob can delay access activation even after employment has formally begun.
Mobile credentials can simplify this process if the selected platform supports secure remote enrolment and compatible readers. Administrators can provision an authorized device, assign door permissions and deactivate the credential when access is no longer required.
However, mobile entry introduces its own dependencies. Smartphone battery condition, device loss, supported operating systems, NFC or Bluetooth functionality, and application provisioning can all affect availability. Some products offer additional capabilities under specific device conditions, but these should be confirmed rather than assumed.
Physical fobs avoid dependence on a personal phone and may be easier to provide to temporary personnel. Their disadvantages are physical distribution, replacement, inventory and recovery. A lost fob also needs prompt deactivation in the system.
The selection should follow working conditions:
- Hybrid and remote-first employees: Consider mobile credentials when compatible devices and secure remote issuance are available.
- Fixed on-site personnel: Offer fobs where predictable hardware access is preferable or phone use is restricted.
- Temporary staff and contractors: Choose fobs or temporary mobile credentials according to visit frequency, device policies and return logistics.
- Accessibility and personal-device concerns: Maintain a reasonable alternative for people unable or unwilling to use a personal smartphone for entry.
A dual-credential system should maintain one authoritative access record for each person. Door permissions must not depend on whether the employee presents a phone or a fob, unless a documented security policy specifically requires that distinction.
The platform should also support a documented contingency when an employee arrives without a functioning credential. An identity-verification and temporary-access process is safer than informal credential sharing.
These same credential-management capabilities become particularly valuable when access is needed for a short maintenance visit rather than an ongoing employment relationship.
How Can Facilities Track Contractors Without Delaying Maintenance Work?
Facilities teams can track contractors efficiently by creating temporary electronic credentials before scheduled maintenance visits. Access should be restricted to authorized doors and service periods, with automatic expiry where supported. This approach reduces manual fob exchanges and repeated reception approvals while retaining useful records of system-recognized access events.
Contractor authorization differs from employee access because it is usually tied to a task and a defined time window. A technician servicing mechanical equipment may need access to a service entrance and plant room without permission to enter offices or records storage.
Traditional processes such as visitor sign-in, key collection and escorted entry can delay work when several approvals must occur after arrival. They may also leave facilities staff responsible for recovering temporary devices once a contractor departs.
A more predictable workflow begins before the service visit. Facilities personnel verify that the contractor is approved, identify the work order, establish the service window and assign only the necessary doors.
Where supported, the access platform can activate a designated credential at the start of the scheduled window and expire it automatically afterward. An administrator should retain a procedure for adjusting access when authorized maintenance runs longer than expected.
Access permissions should reflect approved maintenance zones rather than broad building categories. Areas requiring escorts or specialized authorization need corresponding operating controls; electronic permissions alone cannot enforce every physical supervision requirement.
Audit logs are useful for reconciling access events with work orders. For example, a recorded credential acceptance near a scheduled visit can help verify that the credential was used during the relevant period. It does not establish that the named contractor personally completed the work or that no other person entered.
Access tracking must also respect workplace privacy. The Office of the Privacy Commissioner of Canada’s workplace privacy guidance
Employers should define who can review contractor access records, what those records are used for and how long they are retained. Applicable obligations depend on the jurisdiction and circumstances; there is no single universal retention period for all Canadian commercial access logs.
Combining a maintenance booking with time-restricted credentials and controlled log access creates a useful operational record without turning routine maintenance into an unnecessarily complicated administrative process.
Contractor access is one example of a broader challenge: keeping every digital credential synchronized with the real-world status of the person who holds it.
Key takeaways before establishing an access policy
- Assign a responsible administrator and authoritative personnel record before automating credential changes.
- Ensure role changes remove obsolete door permissions rather than simply adding new privileges.
- Treat deactivation, physical token recovery and periodic permission review as separate controls with different evidence requirements.
How Can Canadian Organizations Manage Digital Access Credentials as Staff Changes?
Canadian organizations should manage digital access credentials through a documented process linked to hiring, job changes, leave and termination. Each personnel event should trigger a review of required door permissions, with revocation timing based on the actual security circumstances. Centralized authorization records, clear ownership and recurring reviews help prevent former employees or transferred personnel from retaining unnecessary access.
Electronic locks cannot compensate for delayed administrative decisions. If human resources records an employee departure but the facilities team receives the information later, the credential may remain authorized throughout the intervening period.
The solution is to define responsibility and timing for each employment event before enabling routine access. An employee should receive only the doors required for the assigned role, and any temporary access should have an identifiable expiry or review condition.
Offboarding requires coordinated timing. An involuntary departure involving an immediate security concern may justify deactivation coordinated with the termination meeting. A planned departure may allow access until an agreed final working time, provided the arrangement matches the employer’s risk assessment and established policy.
The departure record should distinguish several actions:
- Confirm the employee’s final authorized access time and the person approving it.
- Deactivate applicable electronic credentials and verify that connected controllers or offline devices have applied the change.
- Remove or invalidate mobile credentials in the management platform and complete any necessary device-side actions supported by the system.
- Recover issued fobs, badges and keys, recording any unreturned items.
- Transfer responsibility for door schedules, administrative accounts and access approvals maintained by the departing employee.
Administrative revocation and physical recovery are not equivalent. A disabled fob may no longer grant entry, but an unreturned device remains an inventory and potential reactivation concern. Conversely, recovering a fob does not necessarily remove additional mobile or duplicate credentials assigned to the same person.
Role changes require similar discipline. An employee promoted to a management position might need access to a new secure area, but permissions from a previous assignment should not automatically remain active. Repeatedly adding rights without removing obsolete ones creates excessive cumulative authorization.
Canadian workplaces with seasonal personnel, summer hires or recurring contract assignments should define expiry conditions at issuance wherever the platform supports them. This reduces dependence on individual administrators remembering every contract end date.
Periodic reviews should compare current permissions against actual job responsibilities. Department managers can confirm business need, while facilities or security administrators verify that the access platform reflects approved decisions.
The ePACS security-control framework referenced earlier supports maintaining authorized-access lists, reviewing permissions and removing individuals when access is no longer required. Its review frequencies and revocation timing are organization-defined rather than fixed universal schedules.
Finally, door-event records containing identifiable employee information require appropriate privacy governance. Employers should document permitted purposes, restrict administrative access and apply retention rules appropriate to their activities and applicable Canadian federal or provincial law.
Before selecting or expanding a platform, prepare an approved door inventory, identify who authorizes each access group and test the complete process with a representative hire, role change and departure. This provides a practical basis for evaluating suppliers and commissioning a system without disrupting daily operations.
Can electronic access control be installed without replacing every existing office door?
Yes, provided existing doors and frames are compatible with the selected hardware and applicable fire and building requirements. Wireless electronic locks, compatible electric strikes and reusable reader infrastructure may reduce the need for major construction. Every opening still requires an individual suitability assessment.
Will employees be locked out if the access control network fails?
Not necessarily. Some systems allow controllers to make local authorization decisions using previously synchronized credentials, while others depend on network connectivity for particular functions. Buyers should verify offline operating capabilities, power-loss behaviour and approved fallback procedures before deployment.
Do all electronic office locks need to unlock when power is lost?
No. A fail-secure component may be appropriate where an independent, compliant mechanism permits required egress. Other locking arrangements must release under specified conditions. The complete door assembly must comply with applicable building and fire requirements, including any approved special-egress provisions.
Can a Canadian business retain access logs indefinitely for security purposes?
Indefinite retention should not be assumed acceptable. Where access events identify individuals, applicable privacy requirements may govern collection, use, access and retention. Organizations should document legitimate purposes, establish an appropriate retention schedule and determine which federal or provincial rules apply to their workplace.
What should be included in an access control supplier’s commissioning documentation?
A useful commissioning package includes the door inventory, installed hardware and controller configuration, credential testing results, approved exit-operation and power-loss test records, relevant integration checks, administrative procedures and outstanding issues. Facilities personnel should confirm these deliverables before accepting the installation and retiring legacy access arrangements.